Static Application Security Testing Github What Is SAST All About Static Application Security Testing Mend What Is IAST Interactive Application Security Testing Acunetix Blog Dynamic Application Security Testing Tudip What Is Static Application Security Testing Kiuwan Data Theorem Named A Visionary In 2022 Gartner Magic Quadrant For These open source projects and static application security testing SAST solutions bring a wide array of additional security tools directly into the developer workflow ensuring that vulnerabilities can be identified and fixed before they are committed to the code base You can enable these additional capabilities on your public repository today
These include static application security testing SAST dynamic application security testing DAST software composition analysis SCA and interactive application security testing IAST among others Such tools empower individual developers to become security experts bypassing the frustration and wasted time and Find and fix security issues in your code before they reach production with static application security testing SAST See how it works Secret scanning Prevent unauthorized access and breaches by watching your repositories for known secret formats that notify you as soon as secrets are found See how it works Dependency review
Data Theorem Named A Visionary In 2022 Gartner Magic Quadrant For SAST Static Application Security Testing SAST Vs DAST Static Application Security Testing Dynamic Appknox Static Application Security Testing SAST Onefede What Is Static Application Security Testing SAST SNS Blog Why Is Static Application Security Testing Critical First Line Software Static Application Security Testing SAST Basics What Is Static Application Security Testing And How Is SAST Used The Forrester Wave Static Application Security Testing Micro Focus
Static Application Security Testing Github
 Static Application Security Testing Github
https://www.mend.io/wp-content/media/2022/11/SAST-blog-Image.webp
Code scanning is GitHub s application security testing interface It s home to GitHub s static analysis solution CodeQL a semantic analysis engine that can uncover not just known vulnerabilities but unknown variations potentially unsafe coding practices and other code quality issues
Pre-crafted templates offer a time-saving option for producing a diverse range of files and files. These pre-designed formats and layouts can be utilized for numerous personal and expert tasks, consisting of resumes, invites, leaflets, newsletters, reports, presentations, and more, enhancing the material production procedure.
Static Application Security Testing Github
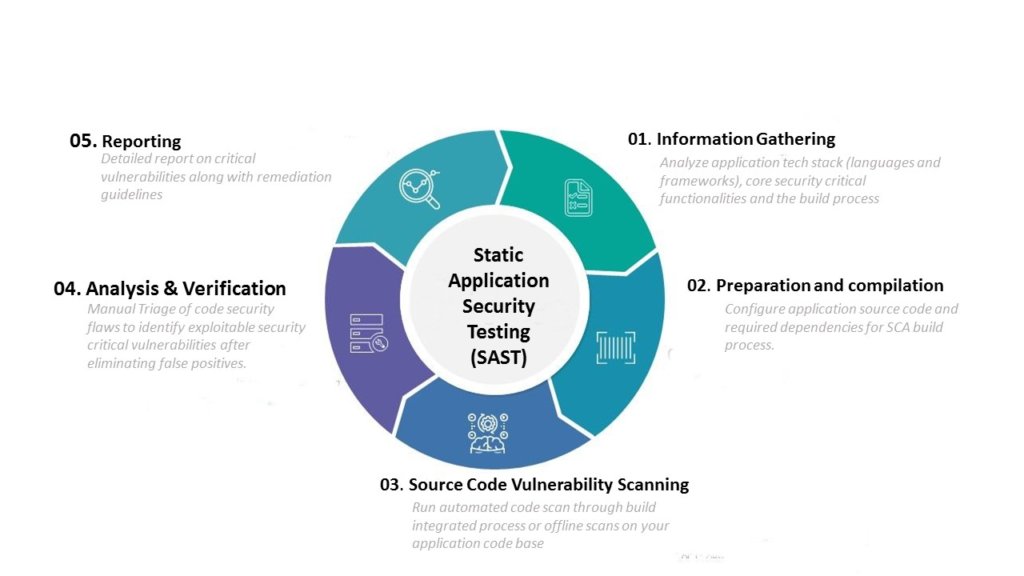
Top 10 Static Application Security Testing SAST Tools In 2022 Spectral

SAST Static Application Security Testing

SAST Vs DAST Static Application Security Testing Dynamic

Appknox Static Application Security Testing SAST Onefede

Why Is Static Application Security Testing Critical First Line Software

Static Application Security Testing SAST Basics

GitHub insidersec insider Static Application Security Testing SAST engine focused on covering the OWASP Top 10 to make source code analysis to find vulnerabilities right in the source code focused on a agile and easy to

This document describes process of running static application security testing SAST on the code generated by OutSystems from the export of source code to analyzing the results n When dealing with the static code analysis process there are some architecture considerations to be taken into account namely when using OutSystems cloud or self

Static application security testing SAST scans binary code or application source code when the application is not running to find vulnerabilities based on design or implementation Dynamic application security testing DAST tests running web applications for security issues by mimicking the same techniques that malicious

Static Application Security Testing SAST The whitepaper A Seismic Shift in Application Security explains how 4 of the top 6 attacks were application based Download it to learn how to protect your organization

How static application security testing SAST can keep your software secure August 9 2022 1 min read Discover what SAST is why it can keep your proprietary code safe and how to get started with SAST
GitHub is where people build software More than 100 million people use GitHub to discover fork and contribute to over 330 million projects Application Security Testing Group Skip to content Toggle navigation Sign up Product Actions Automate any workflow Packages Host and manage packages Security Find and fix vulnerabilities How to do Static Application Security Testing SAST in GitHub and to succeed with this critical security configuration Part 5 12 In this video Padi an
GitHub Actions enables automated security testing in your continuous integration continuous deployment CI CD pipeline This feature brings security testing up to speed with software development as it allows you to automatically test your code for security issues at the same time as your regular testing processes like unit and