Spring Security Oauth2 Jwt Refresh Token OAuth 2 0 Refresh Token Best Practices JWT Refresh Token Implementation In Node JS Reactjs Spring Security OAuth2 New Authorization Server With PKCE Spring Boot Security Jwt Access And Refresh Tokens Jwt Flow Hot Sex Picture Build JWT Refresh Token with Spring Security in the Spring Boot Application You can know how to expire the JWT Token then renew the Access Token with Refresh Token in HttpOnly Cookie The instruction can be found at Spring Security Refresh Token with JWT
OAuth2RestTemplate should be used instead of RestTemplate when JWT authentication is required You can set AccessTokenProvider to it which will tell how the JWT token will be retrieved oAuth2RestTemplate setAccessTokenProvider new MyAccessTokenProvider In class implementing AccessTokenProvider you need to implement obtainAccessToken and refreshAccessToken methods An implementation of an AbstractOAuth2Token representing an OAuth 2 0 Refresh Token A refresh token is a credential that represents an authorization granted by the resource owner to the client It is used by the client to obtain a new access token when the current access token becomes invalid or expires or to obtain additional access tokens with identical or narrower scope
Jwt Flow Hot Sex Picture Using Refresh Token In Asp Net Core Web API Project TechMeet360 OAuth 2 0 Resource Server JWT Spring Security spring Security OAuth2 Token Jwt Java CSDN OAuth2 Devhaks Spring Security OAuth2 JWT Entry To Actual Combat 20 Password Oauth 2 0 And Openid Connect Owasp Munich Vrogue Spring Security OAuth2 resource id Spring Security Logo Png Lupon gov ph
Spring Security Oauth2 Jwt Refresh Token
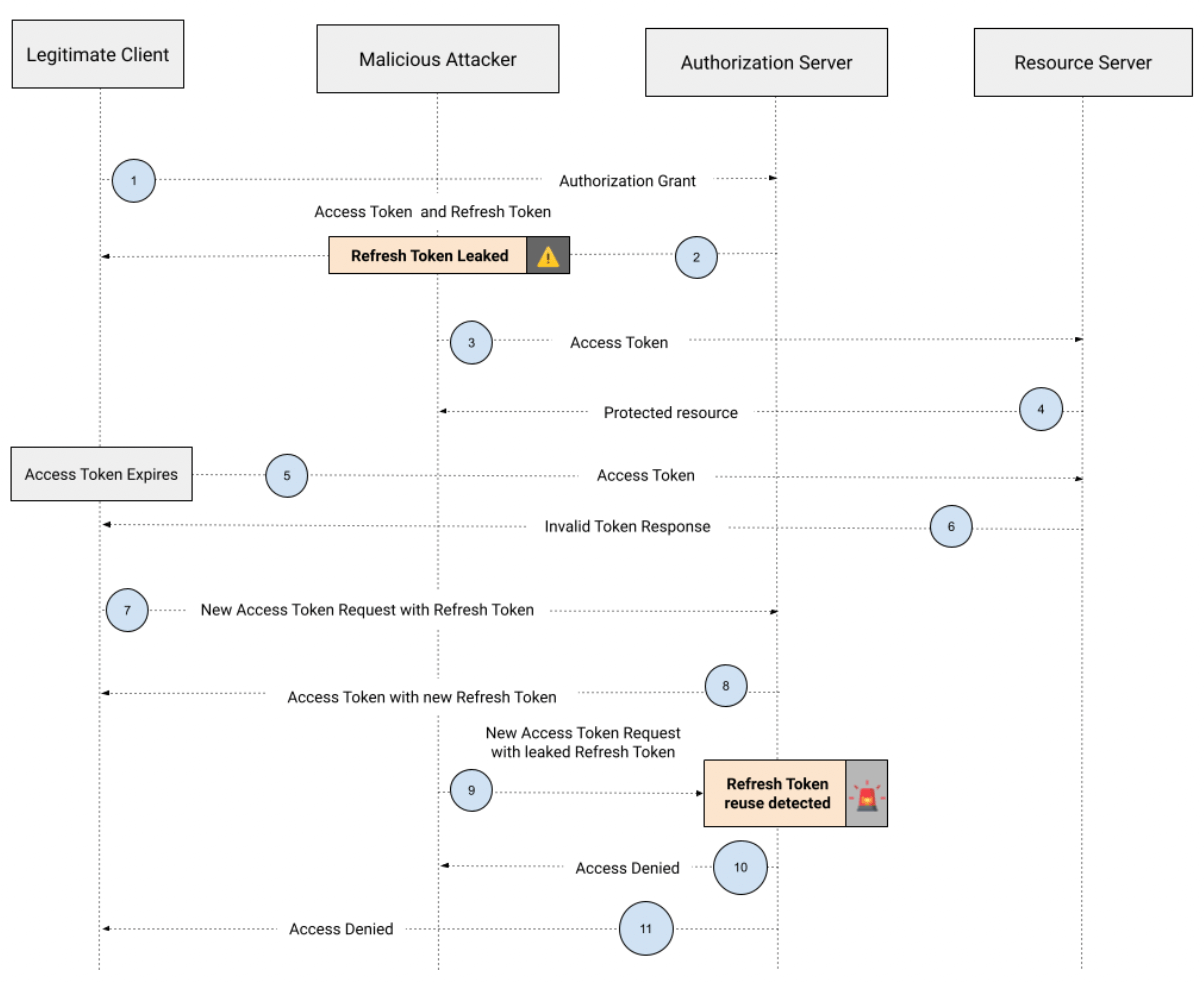 Spring Security Oauth2 Jwt Refresh Token
https://stateful.com/images/blog/blog-oauth-refresh-token-best-practices-2.png
I have configured my spring boot application to to provide oauth2 authorization Configuration public class OAuth2Configuration Configuration EnableResourceServer protected static
Pre-crafted templates provide a time-saving option for developing a varied range of files and files. These pre-designed formats and designs can be utilized for different individual and professional tasks, including resumes, invites, flyers, newsletters, reports, discussions, and more, improving the content development process.
Spring Security Oauth2 Jwt Refresh Token
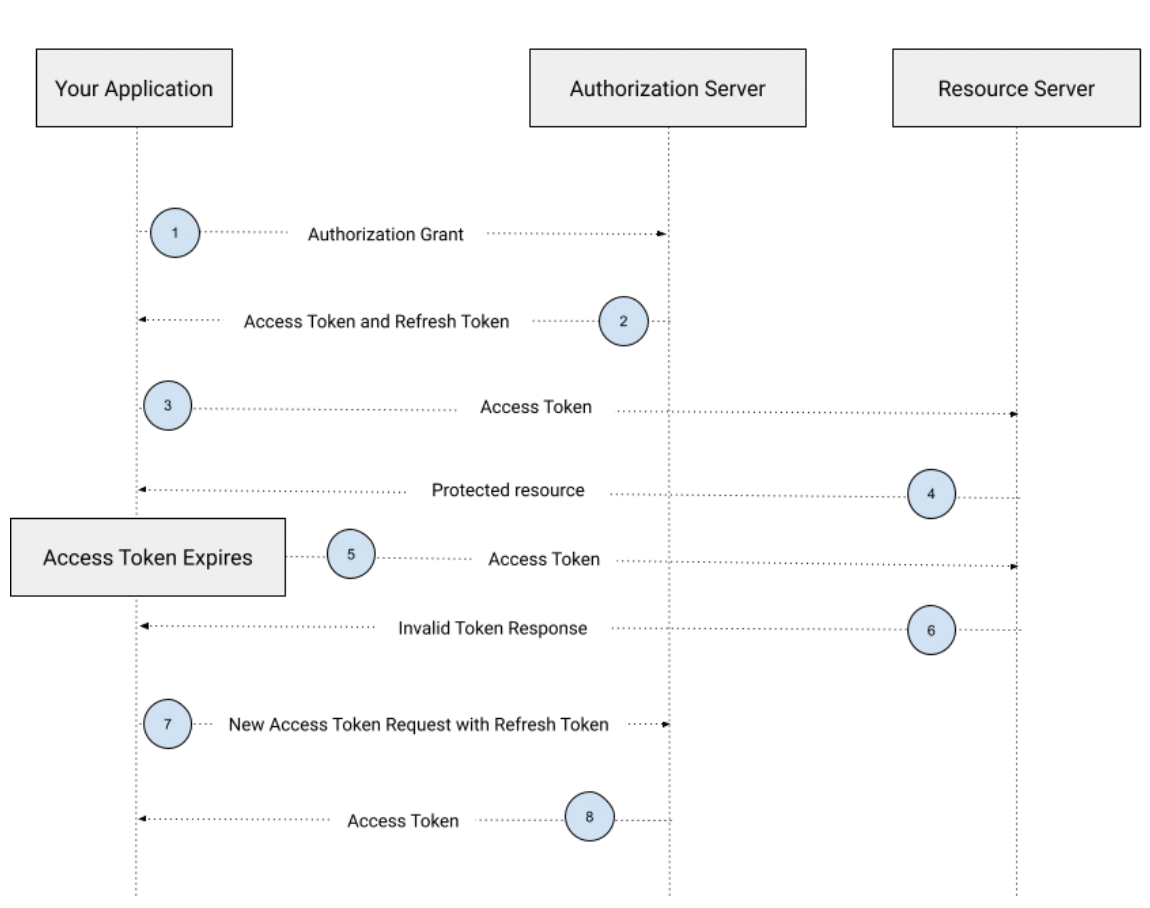
OAuth 2 0 Refresh Token Best Practices Stateful

Using Refresh Token In Asp Net Core Web API Project TechMeet360
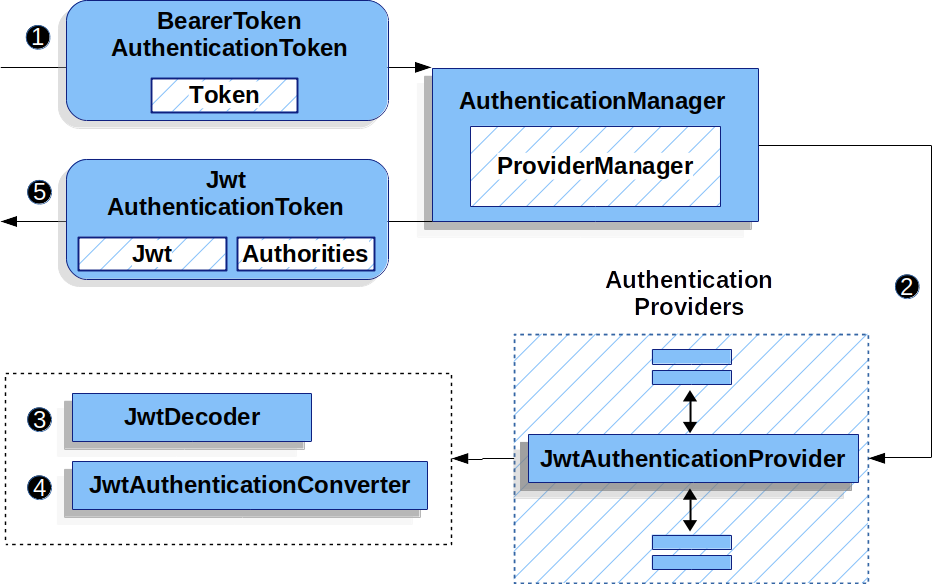
OAuth 2 0 Resource Server JWT Spring Security
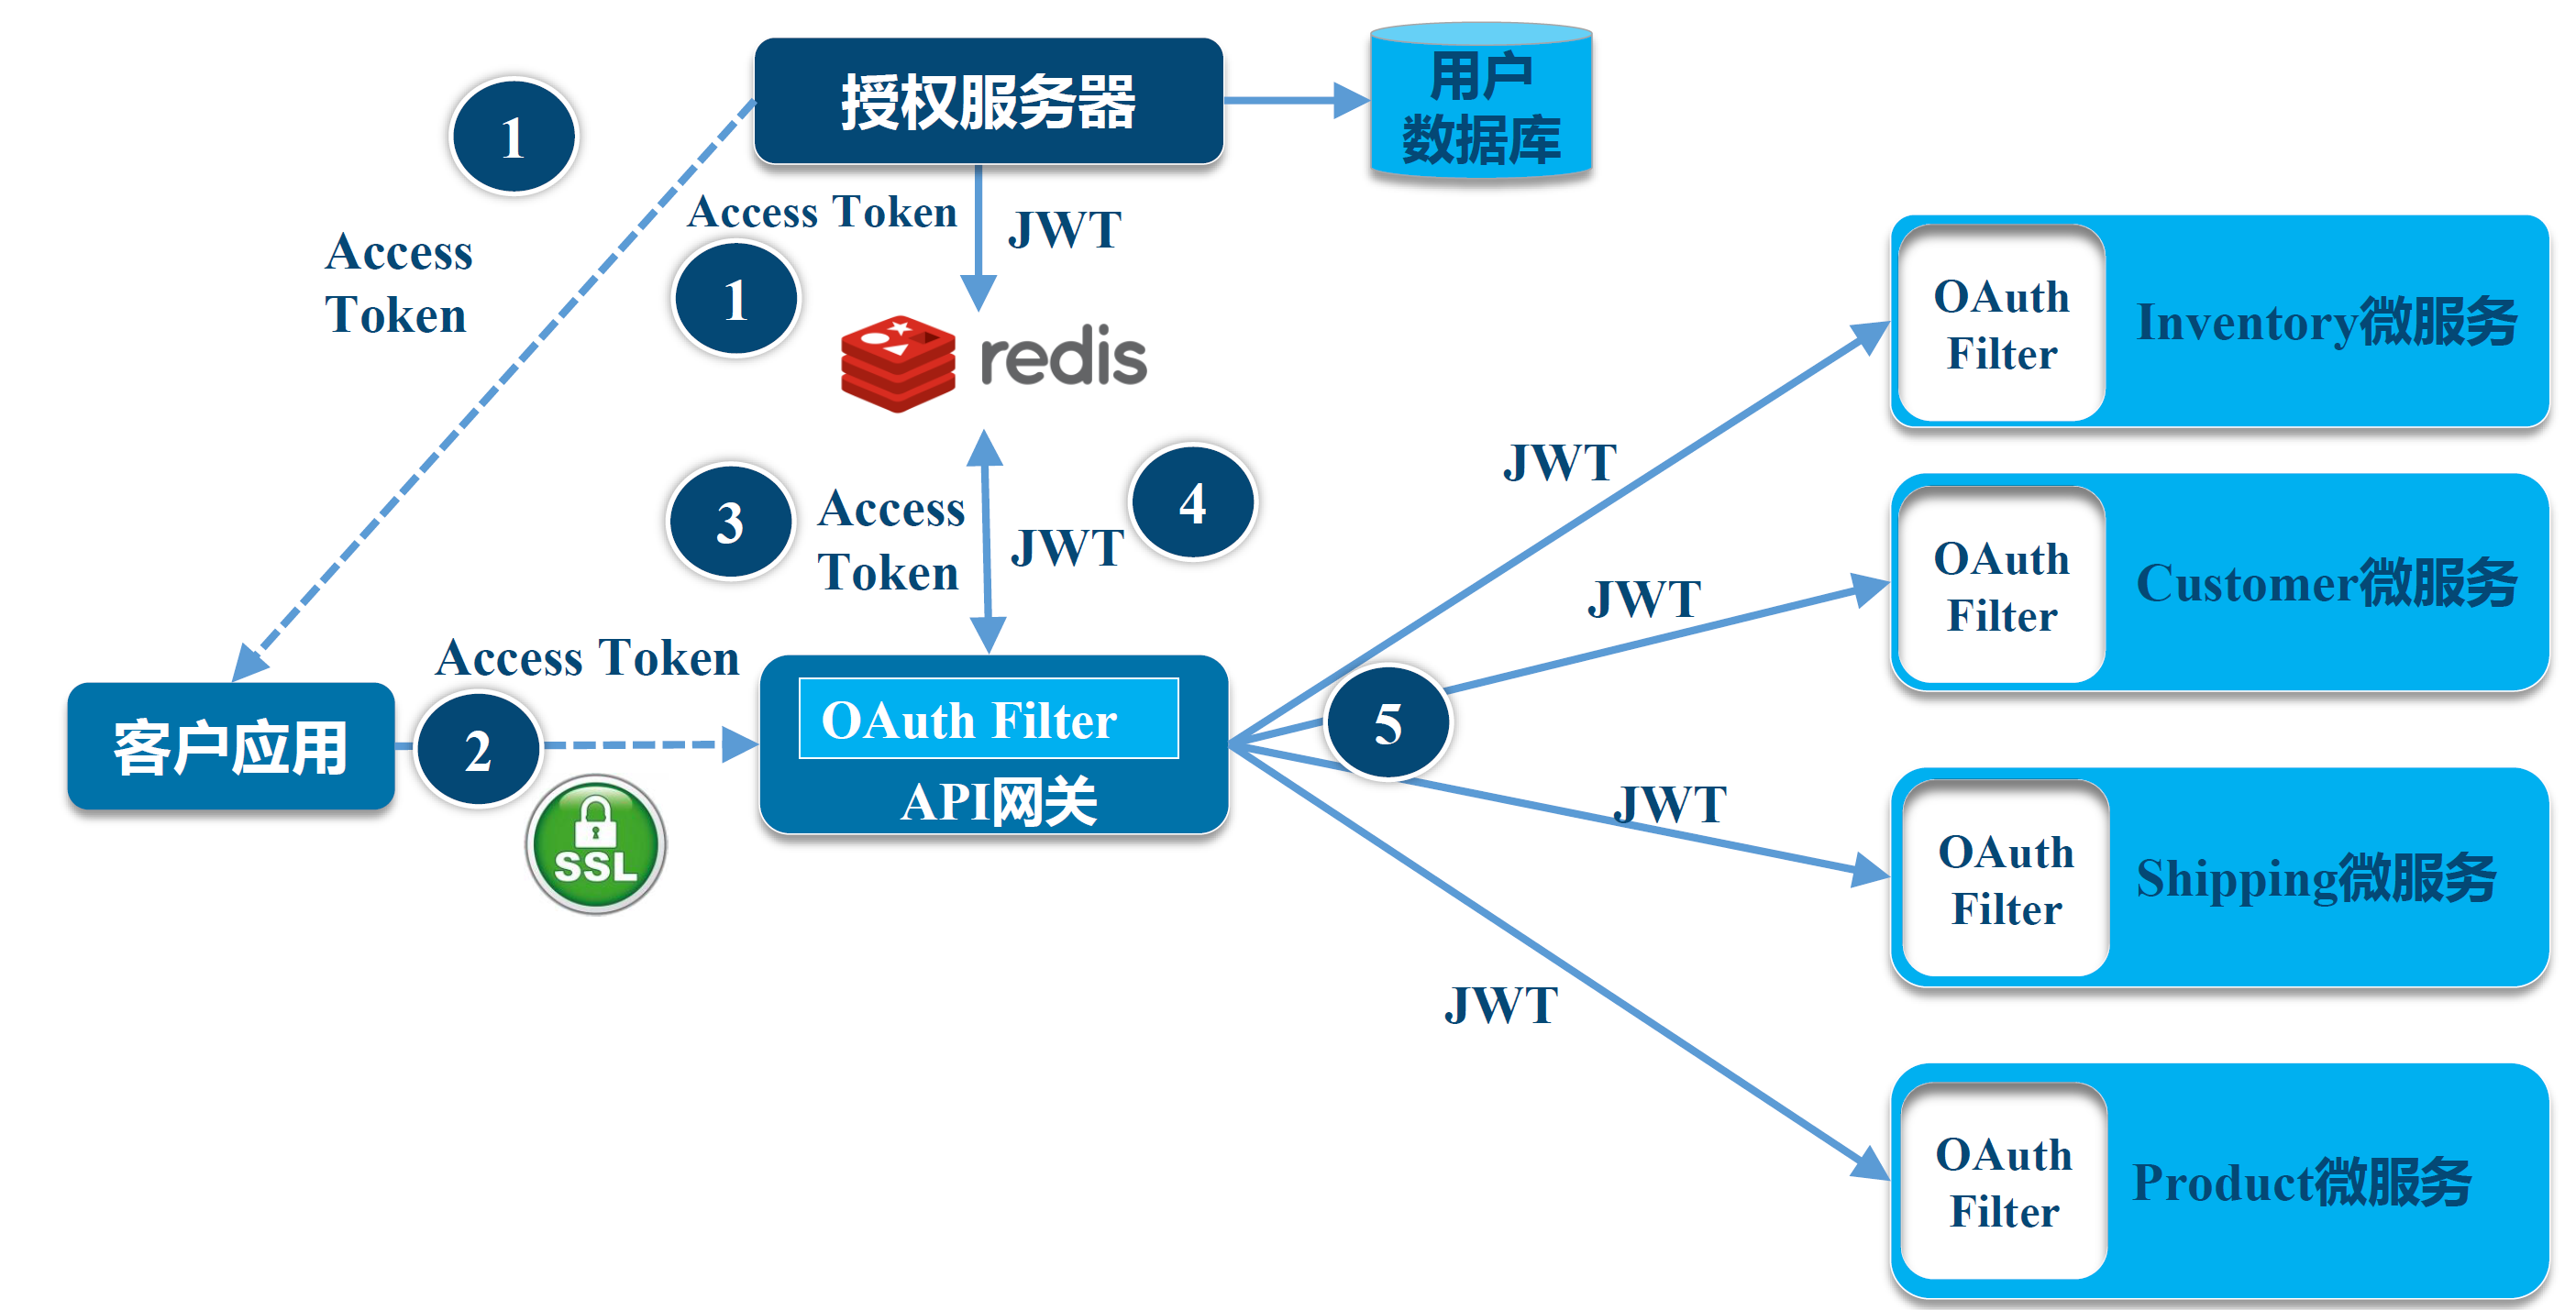
spring Security OAuth2 Token Jwt Java CSDN
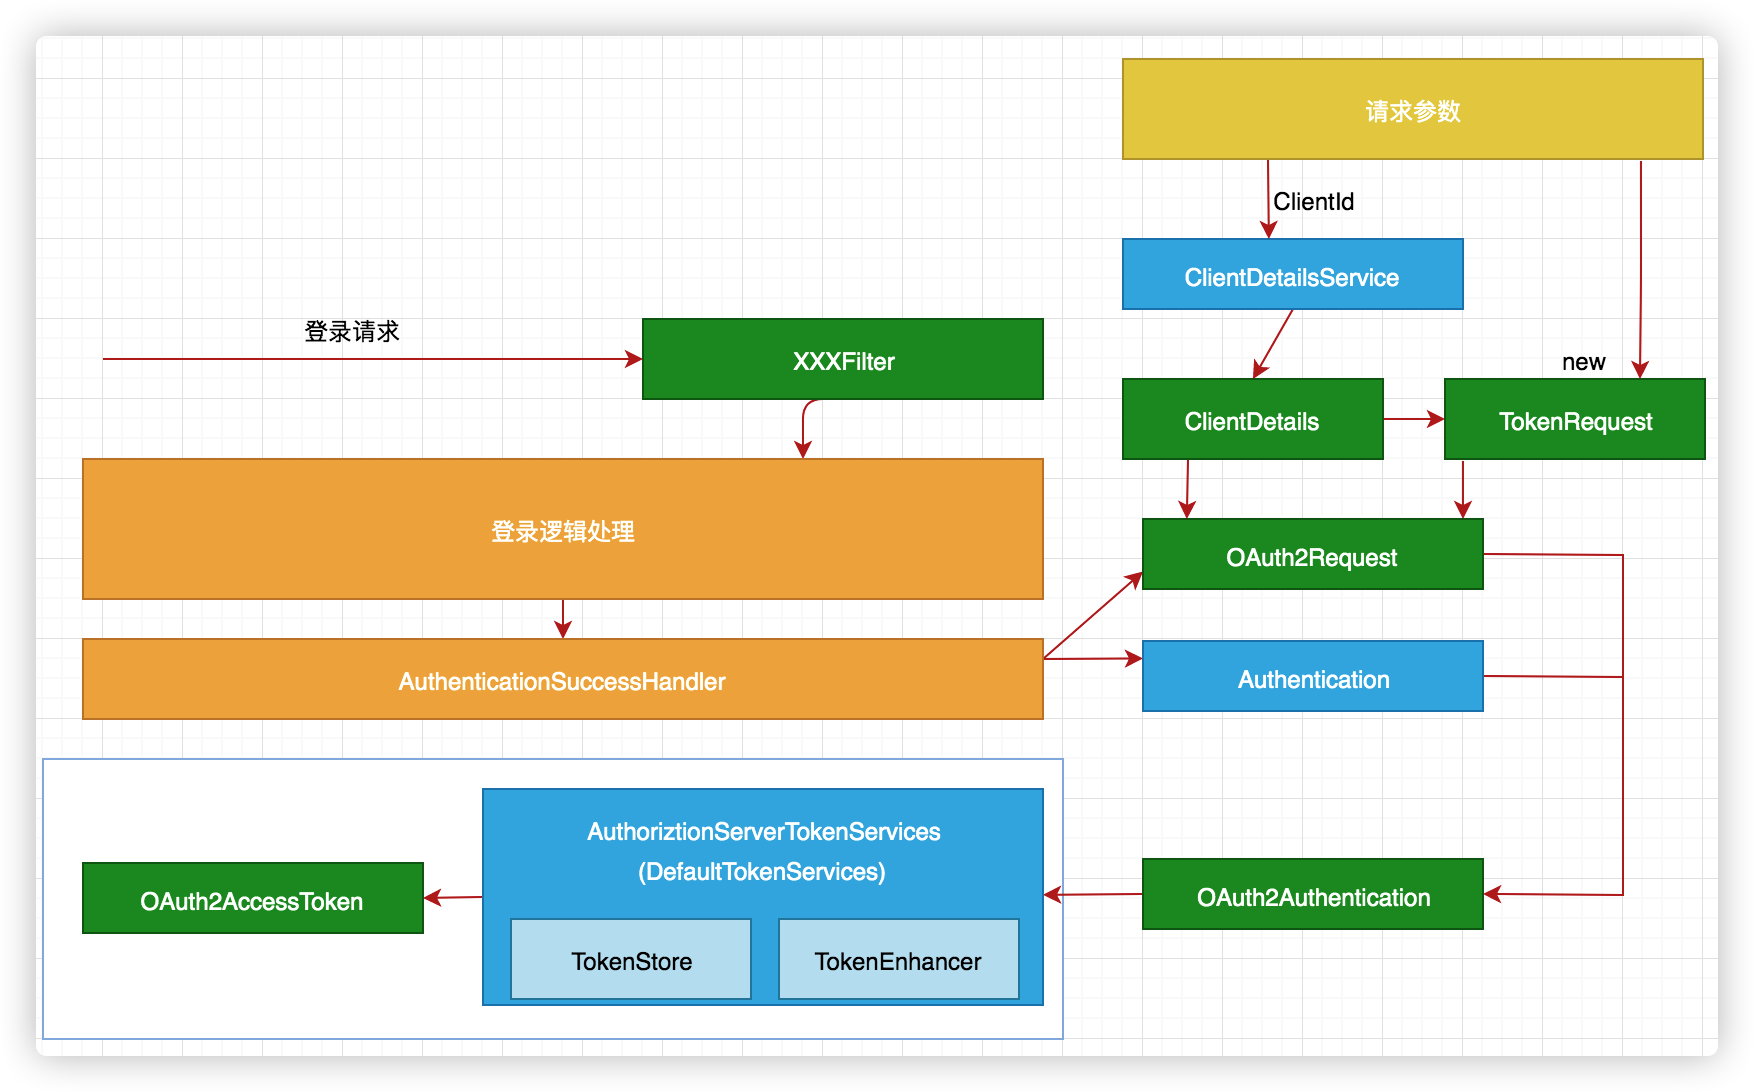
Spring Security OAuth2 JWT Entry To Actual Combat 20 Password
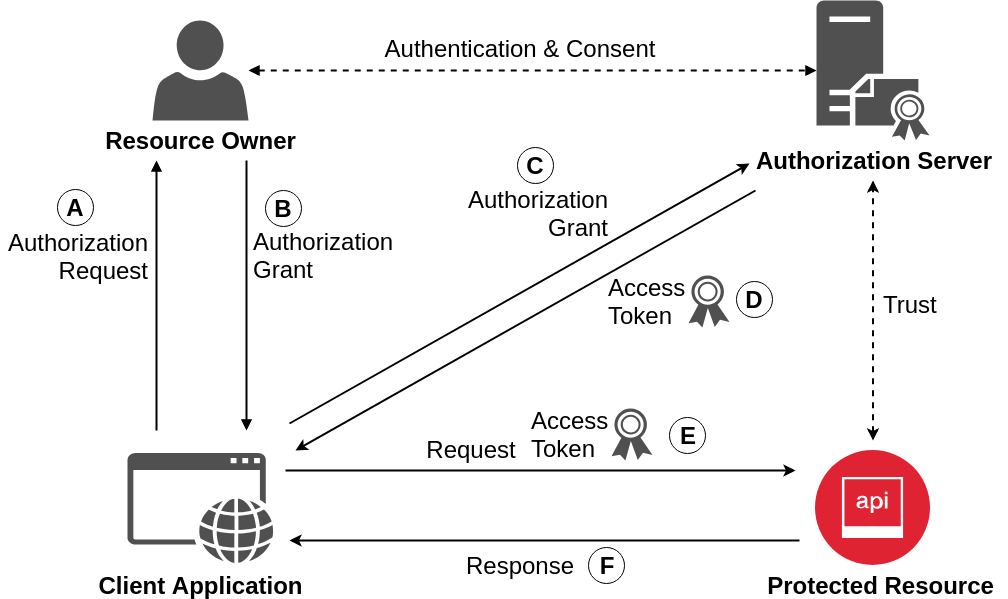
Oauth 2 0 And Openid Connect Owasp Munich Vrogue
Previously the Spring Security OAuth stack offered the possibility of setting up an Authorization Server as a Spring Application We then had to configure it to use JwtTokenStore so that we could use JWT tokens However the OAuth stack has been deprecated by Spring and now we ll be using Keycloak as our Authorization Server

First by intercepting any user request that returns a 401 status code which means the access token is invalid When this occurs if the user has checked the remember me option we ll automatically issue a request for a new access token using refresh token grant type then execute the initial request again

A legal JWT must be added to HTTP Authorization Header if Client accesses protected resources A refreshToken will be provided at the time user signs in If you want to use HttpOnly Cookie for JWT instead kindly visit Spring Security Refresh Token with JWT How to Expire JWT Token in Spring Boot The Refresh Token has different value and expiration time to the Access Token

This way it can be accessed among the additionalParameters in the custom user service the following way String refreshToken String userRequest getAdditionalParameters get OAuth2ParameterNames REFRESH TOKEN Thank you very much johnyka

Spring Security oauth2 with jwt revocation of refresh token I currently have an implementation of spring security with oauth2 running on spring boot It is working as expected and I have set the validity of access tokens to 10 minutes and refresh tokens to 30 days However I would like to be able to invalidate the refresh token if a user
4 Answers When using a WebClient configured correctly as given in the documentation it will automatically be refreshed Spring Security will automatically refresh expired tokens if a refresh token is present This is also supported by the features matrix that refresh tokens are supported The application uses Spring Security and OAuth 2 0 with JWT tokens for authentication and authorization When a user successfully logs in and obtains a JWT token containing the appropriate roles for example ROLE ADMIN access to the protected resource is still denied
1 Overview In this tutorial we ll continue exploring the OAuth2 Authorization Code flow that we started putting together in our previous article and we ll focus on how to handle the Refresh Token in an Angular app We ll also be making use of the Zuul proxy We ll use the OAuth stack in Spring Security 5