Web Application Security Best Practices Owasp Web Application Security Best Practices OWASP Top Ten Web Application Security Best Practices To Stop Threats Add A Certificate To The Trusted Publishers With Intune Without OWASP Top 10 Why It Still Matters Migliori App Android Sicurezza Privacy Web Apr 2 2020 nbsp 0183 32 Get the Most Out of This Course Understand Secure Programming Identify the right security regulations Discover the Open Web Application Security Project OWASP Quiz Check Your Understanding of Security Regulations Prevent Injection Prevent Broken Authentication Protect Data in Transit Protect Data at Rest Stop Broken Access Control
Web May 11 2024 nbsp 0183 32 Raising Security Awareness Another significant benefit of using the OWASP Top 10 in penetration testing is its role in fostering security awareness By systematically targeting and reporting on these top risks you can enlighten your organization or clients about the most pressing web application security threats Web Jun 23 2023 nbsp 0183 32 Snapshots are good Continuous security testing is better Modern enterprise grade security testing for web API business logic and LLMs at the speed of deployment Book a demo However it s important to note that while the OWASP Top 10 is a valuable resource it s not the definitive answer to all security challenges
Migliori App Android Sicurezza Privacy What Is Open Web Application Security Project OWASP Sangfor 7 Web Application Security Best Practices Acunetix OWASP API Security Top 10 A Guide To Protecting Your APIs Across The Finom t s Karom Ennek Eredm nyek nt Owasp Top Ten 2020 Fell p Ide lis 11 Web Application Security Best Practices You Need To Know Mobindustry OWASP Top 10 The Most Critical Web Application Security Risks Top 15 Application Security Best Practices OWASP Top 10 Understanding The Most Critical Application Security Risks
Web Application Security Best Practices Owasp
 Web Application Security Best Practices Owasp
https://blog.talent500.co/wp-content/uploads/2023/12/[email protected]
Web Input validation is a crucial part of application security Input validation failures can result in many types of application attacks These include SQL Injection Cross Site Scripting Command Injection Local Remote File Inclusion Denial of Service Directory Traversal LDAP Injection and many other injection attacks
Pre-crafted templates provide a time-saving solution for creating a varied variety of files and files. These pre-designed formats and designs can be used for numerous individual and expert jobs, including resumes, invites, flyers, newsletters, reports, discussions, and more, streamlining the material creation procedure.
Web Application Security Best Practices Owasp

10 Web Application Security Best Practices Argos Infotech
What Is Open Web Application Security Project OWASP Sangfor
7 Web Application Security Best Practices Acunetix

OWASP API Security Top 10 A Guide To Protecting Your APIs Across The
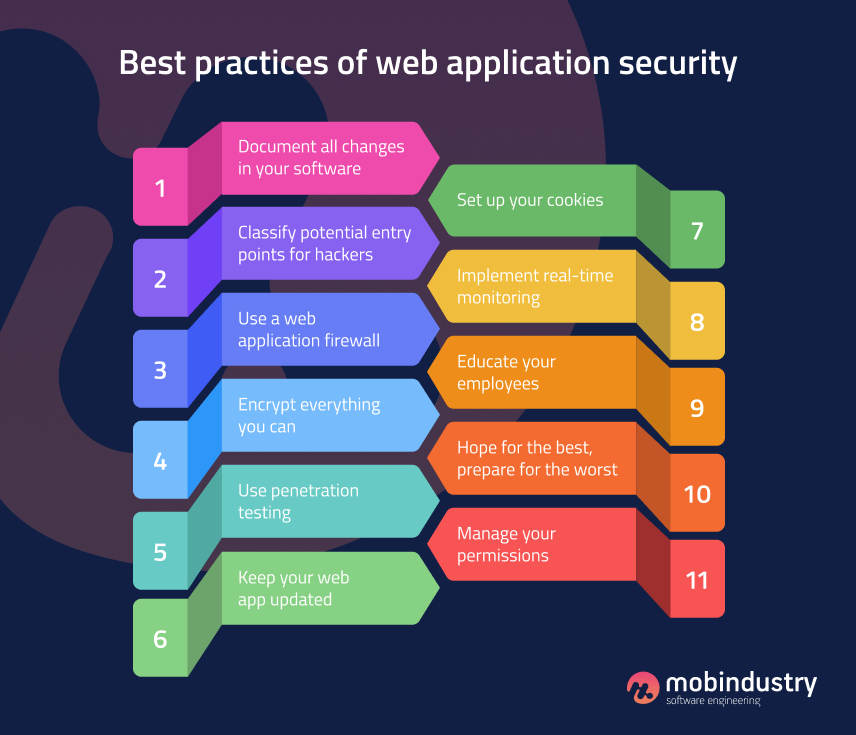
11 Web Application Security Best Practices You Need To Know Mobindustry

OWASP Top 10 The Most Critical Web Application Security Risks

Web Web services need to ensure that the output sent to clients is encoded to be consumed as data and not as scripts This gets pretty important when web service clients use the output to render HTML pages either directly or indirectly using AJAX objects Rule All the rules of output encoding applies as per Cross Site Scripting Prevention Cheat Sheet

Web This work is licensed under the Creative Commons Attribution ShareAlike 2 5 License To view a copy of this license visit http creativecommons licenses by sa 2 5

Web Appendix F Leveraging Dev Tools Edit on GitHub WSTG v4 2 on the main website for The OWASP Foundation OWASP is a nonprofit foundation that works to improve the security of software

Web Definition of the people responsible for security ideally the WAF application manager Step 2 Baseline security for all web applications mostly blacklisting using vendor signatures monitor for false positives negatives and get rid of them Step 3

Web Nov 14 2019 nbsp 0183 32 Security And The OWASP Top 10 OWASP stands for Open Web Application Security Project It is a non profit organization that regularly publishes the OWASP Top 10 a listing of the major security flaws in web applications For example one of the lists published by them in the year 2016 looks something like this For each of the
Web Nov 11 2023 nbsp 0183 32 Introduction Web applications have become an integral part of our digital world serving as gateways to information communication and services However this digital realm is fraught with Web Activity Conduct security awareness training for all roles currently involved in the management development testing or auditing of the software The goal is to increase the awareness of application security threats and risks security best practices and secure software design principles Develop training internally or procure it externally
Web Mar 17 2023 nbsp 0183 32 In this blog post we ll discuss ten essential web application security best practices that you need to know to secure your web applications and keep your data safe 1 Secure Coding Practices