Splunk Log Search Examples Splunk Log Observer Splunk Splunk Cloud Architecture Mindmajix Example Search Splunk Splunk Log Analytics Available In Lower cost Light Version InfoWorld Troubleshooting Splunk Part 3 Splunk Internal Log Analysis For HTTP Dec 13 2012 nbsp 0183 32 I am attempting to search a field for multiple values this is the syntax I am using lt mysearch gt field value1 value2 table time field The doesn t work but I assume there is
Discover Community and Learning Resources for your Role Welcome to your curated Learning Paths Whether you re new to Splunk or looking to deepen your expertise these role based Apr 5 2020 nbsp 0183 32 I m running the below query to find out when was the last time an index checked in However in using this query the output reflects a time format that is in EPOC format I d like to
Troubleshooting Splunk Part 3 Splunk Internal Log Analysis For HTTP Ship Data To Splunk By Using The Splunk Add on For Log Service Log Mint Security Splunk Delivery Models Blogs Why Should You Use Splunk For Log Analysis TO THE NEW Blog Search Chart And Report Examples Splunk Knowledgebase Splunk Logging Best Practices Splunk Logback Mindmajix Splunk Field Extraction And Report For Cisco AnyConnect VPN Failures What Is Splunk Centralized Log Management DevOps Splunk Cloud Data Comparison LCE Splunk Client
Splunk Log Search Examples
 Splunk Log Search Examples
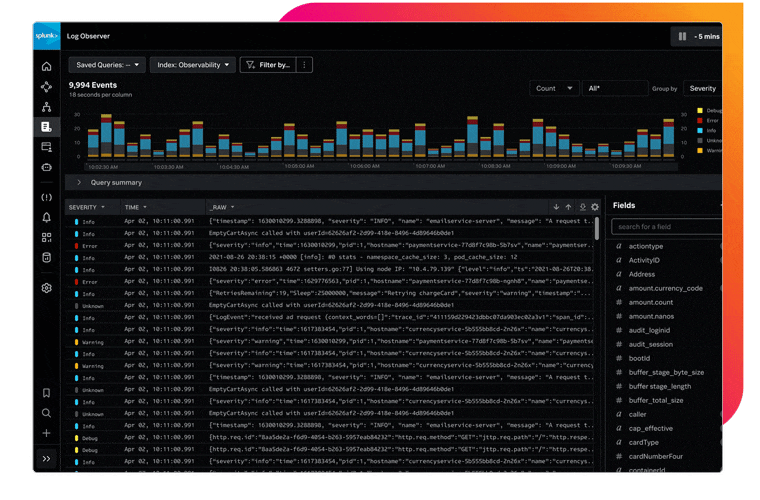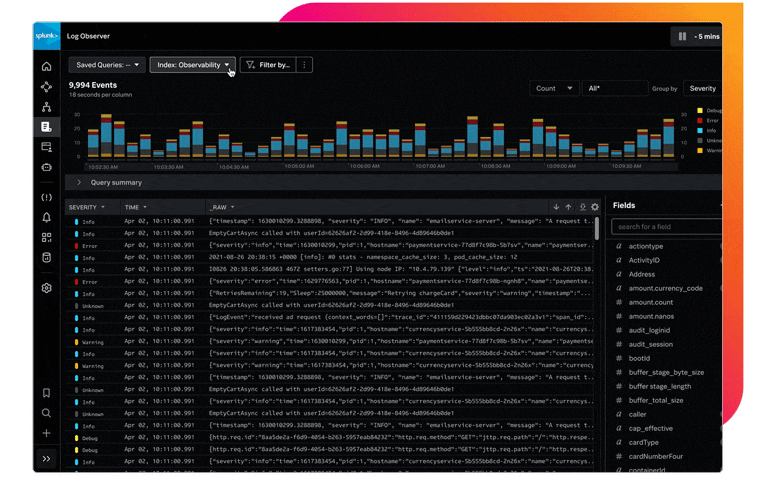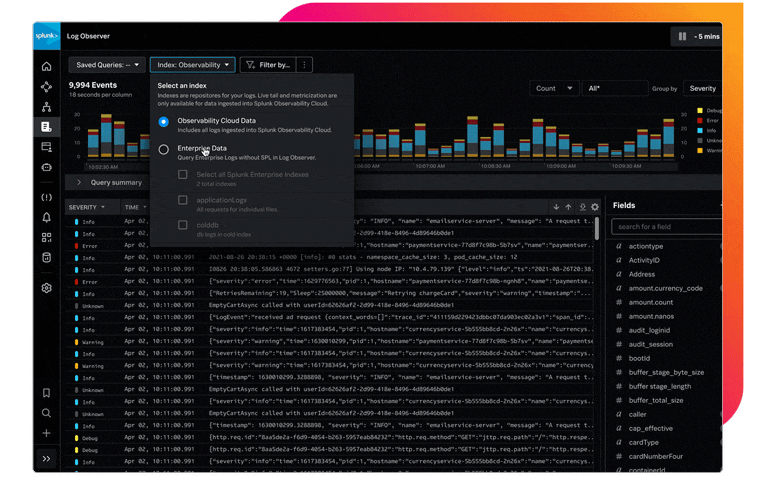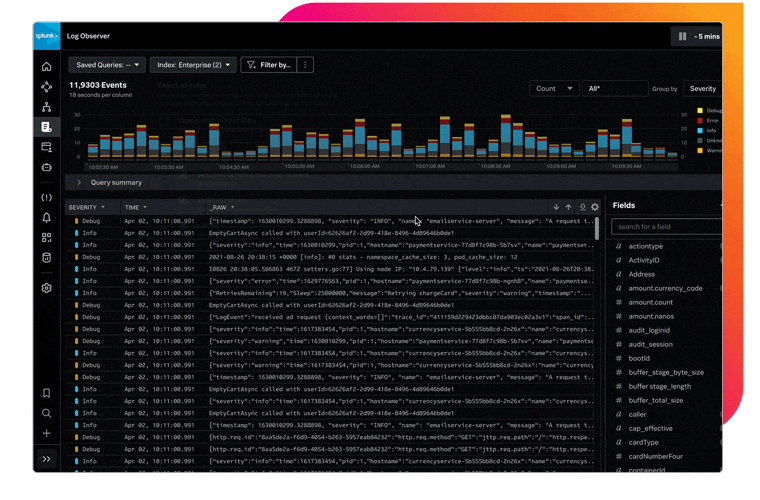
https://www.splunk.com/content/dam/splunk2/en_us/images/screenshots/observability/splunk-log-observer-river-1-content-dashboard-embelishment.gif
Dec 19 2014 nbsp 0183 32 How to convert time to a human readable format and display Time and Date in a single value panel
Templates are pre-designed files or files that can be used for various purposes. They can save time and effort by offering a ready-made format and design for producing different type of material. Templates can be used for personal or professional tasks, such as resumes, invites, leaflets, newsletters, reports, discussions, and more.
Splunk Log Search Examples
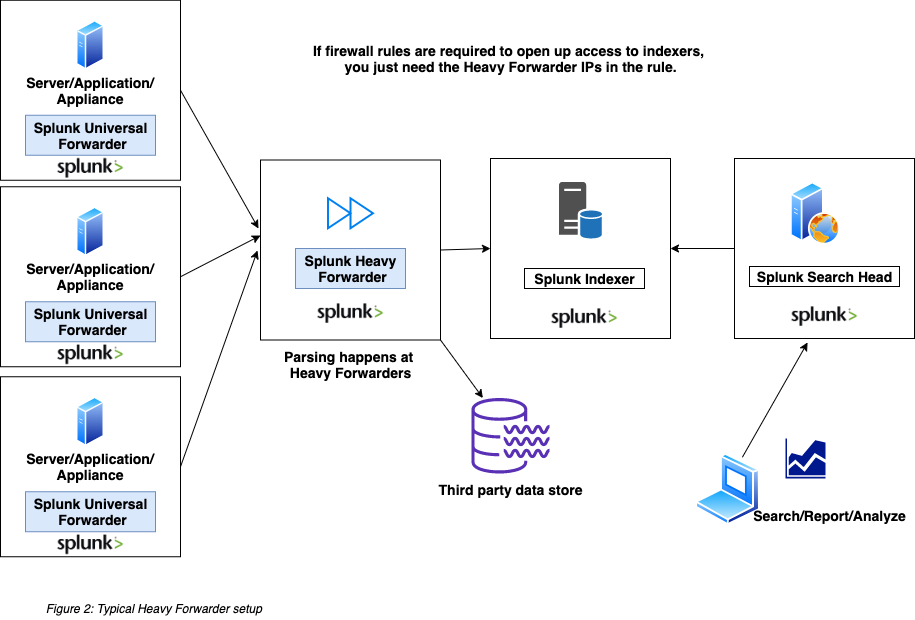
What Is The Difference Between Splunk Universal Forwarder And Heavy

Ship Data To Splunk By Using The Splunk Add on For Log Service Log
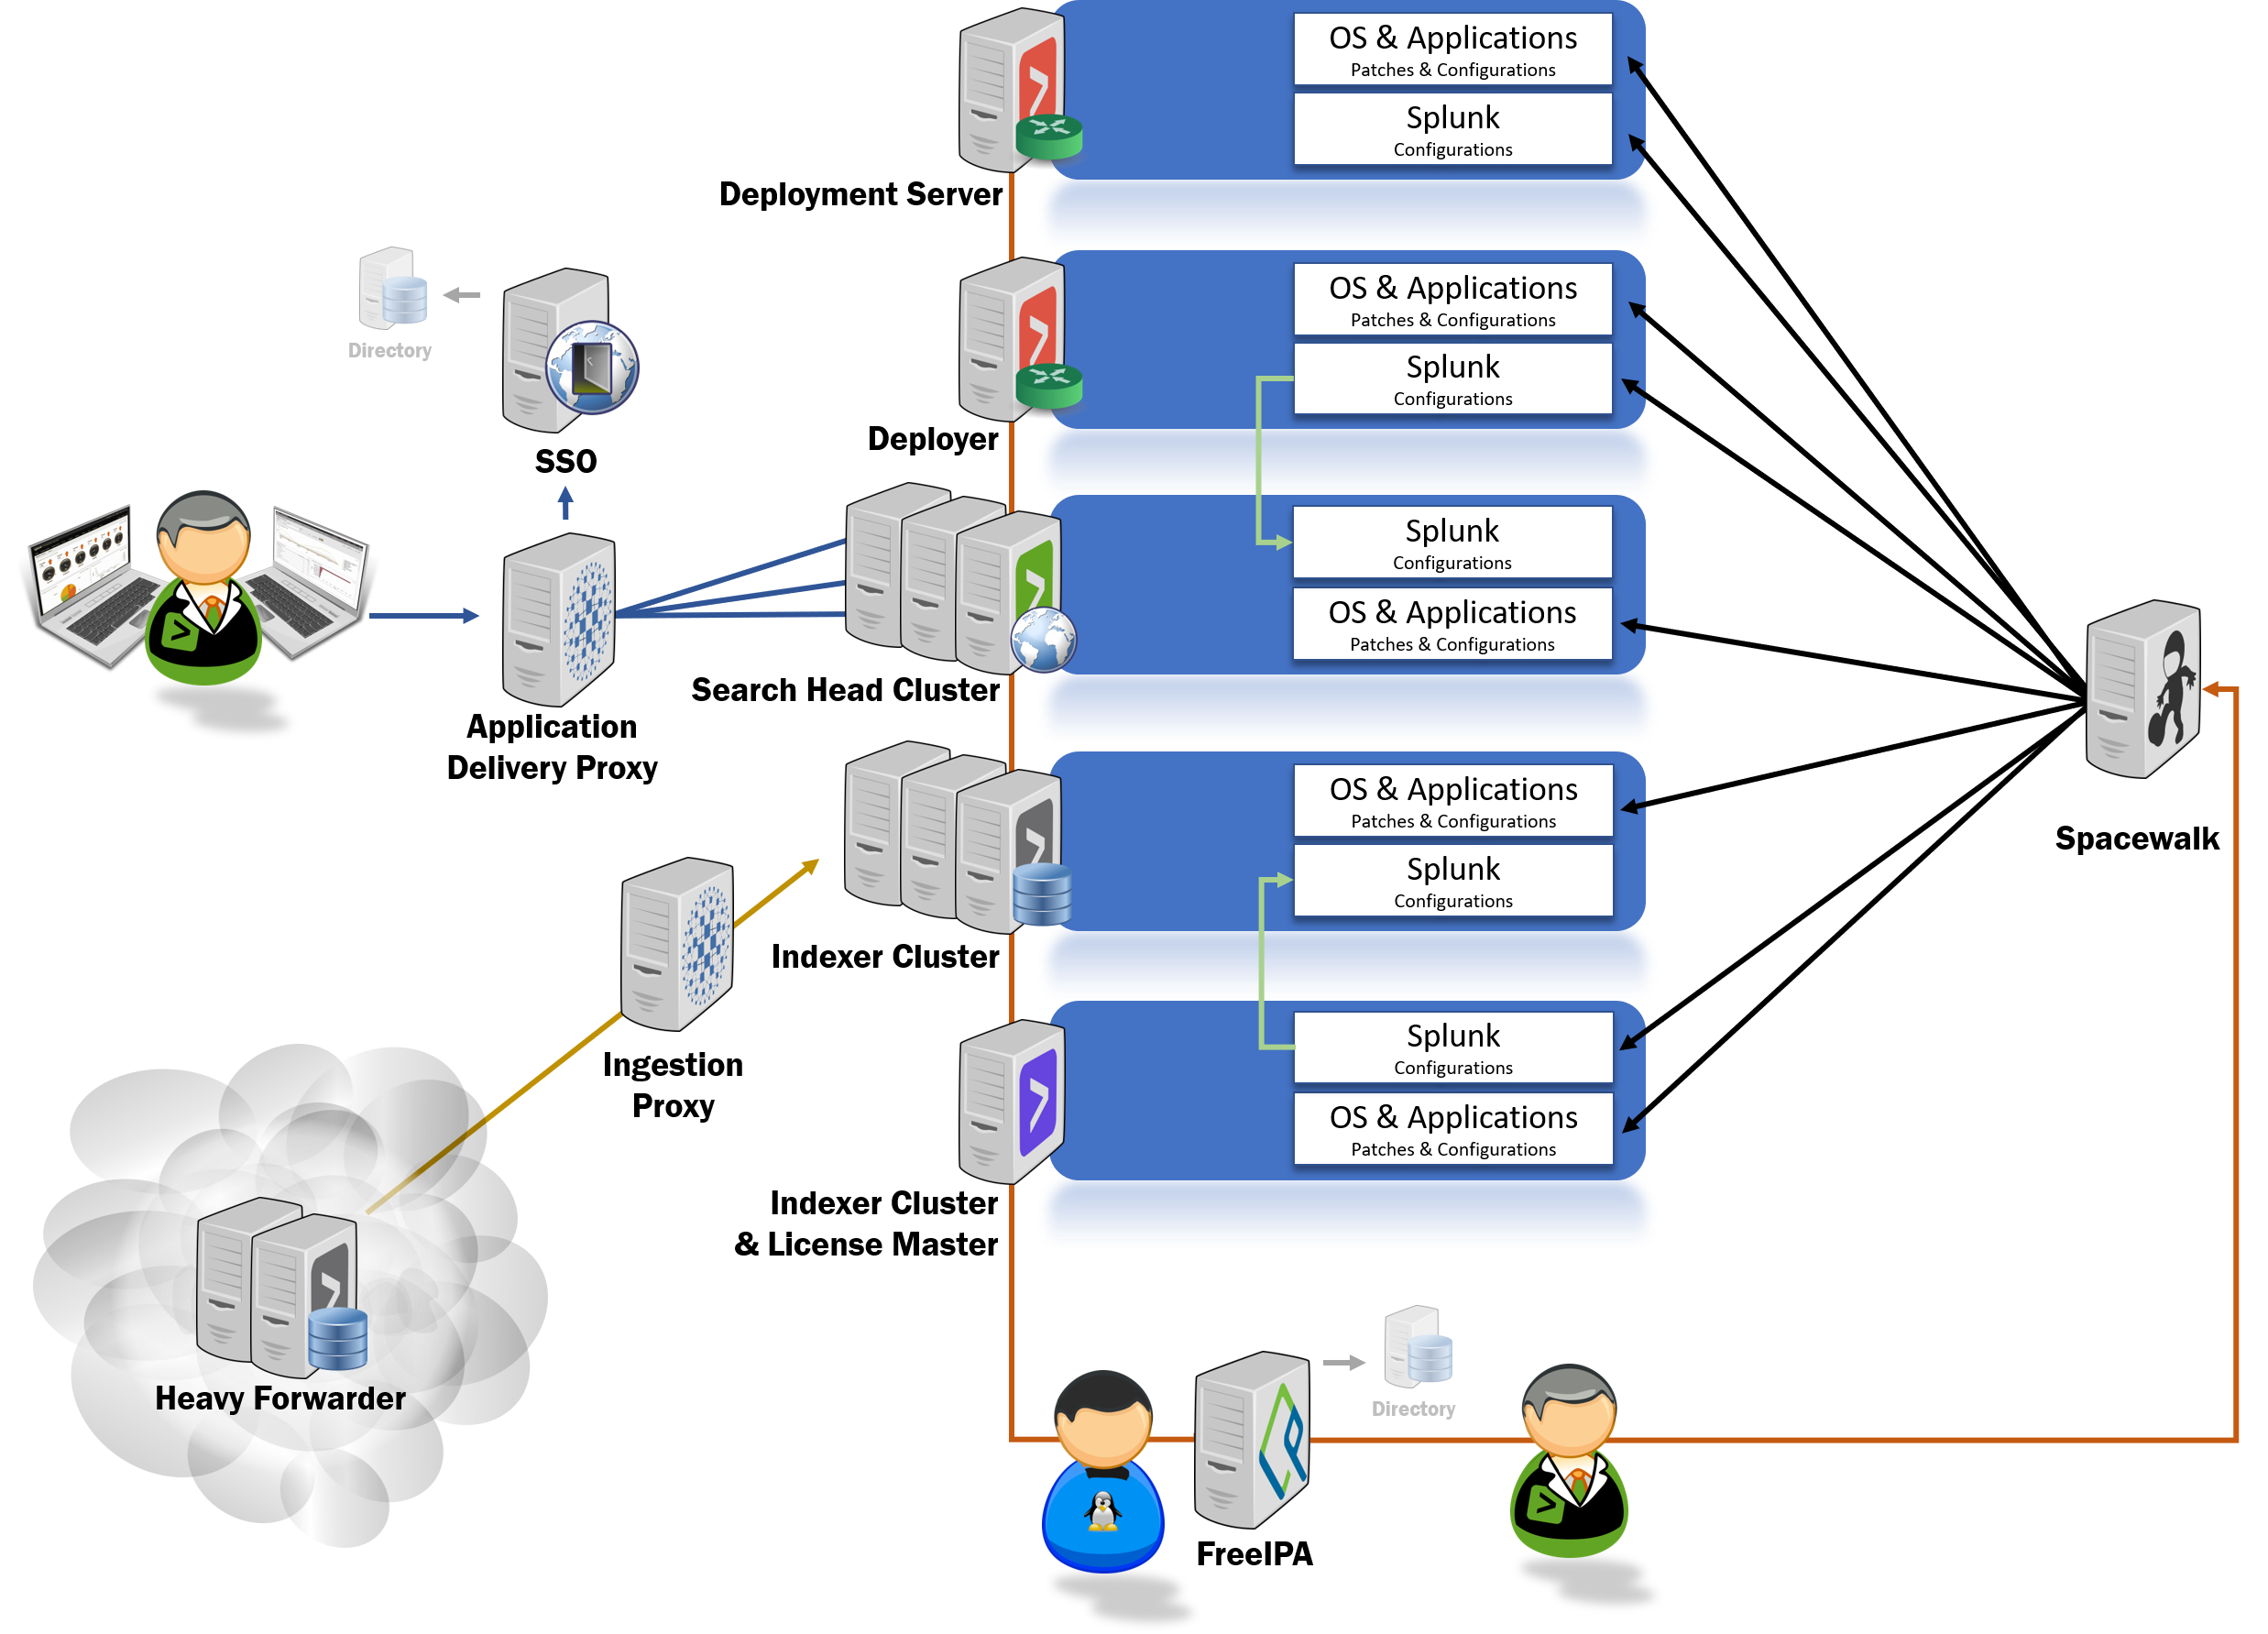
Mint Security Splunk Delivery Models Blogs

Why Should You Use Splunk For Log Analysis TO THE NEW Blog

Splunk Logging Best Practices Splunk Logback Mindmajix

Splunk Field Extraction And Report For Cisco AnyConnect VPN Failures

Oct 19 2012 nbsp 0183 32 Currently i m running this command for 2 days it takes quite a lot of time index stats count by index Is there a better to get list of index Since its like a table created in splunk
Jun 10 2025 nbsp 0183 32 Read our previous announcements to learn more about major updates and upgrade readiness Why is this Important Keeping your app Splunk 10 compatible secures

Calling all Splunk developers custom SPL builders dashboarders and Splunkbase app creators the Builder Bar is back at conf25 and this year we re serving up something fresh a retro

Jan 7 2025 nbsp 0183 32 Using the FIPS certified crypto module that already ships with Splunk is easiest 5 How to plan ahead Sign up for our Splunk Enterprise OpenSSL 3 Beta to ensure your Splunk

Sep 10 2011 nbsp 0183 32 I would like to see the rows of my csv lookup file through a splunk query Is there any option which reads the lookup file and prints all the rows of lookup file
[desc-11] [desc-12]
[desc-13]