Splunk Log Format Example Splunk Log Observer Splunk Tips For Parsing XML Log Files In Splunk Pixelchef Splunk Enterprise Cloud Islamgasw Top Data Analytics Tool Splunk Dashboard Zsah Getting Started With Splunk As An Engineer DZone Big Data Jan 27 2015 nbsp 0183 32 Hi I am brand new to Splunk I ve read up on what I can in the past few days and need some help clarifying some things Our old splunk admin left the company and I ve been
Mar 5 2025 nbsp 0183 32 Please can you confirm if you are trying to pull Splunk data into Power BI or pull Power BI data in to Splunk While there isn t an official guide from Splunk specifically for Jul 23 2024 nbsp 0183 32 I just realized that I lost the Admin password and I need a way to access the system with my Admin credentials
Getting Started With Splunk As An Engineer DZone Big Data Splunk Operational Intelligence InfoGuard Splunk Boss Of The SOC X y D ng Gi i Ph p Thu Th p Log Cho M t Doanh Why Should You Use Splunk For Log Analysis TO THE NEW Blog Splunk SOAR Playbooks GCP Unusual Service Account Usage Splunk Log Management Tools Face Off Splunk Vs Logstash Vs Sumo Logic Splunk Log Observer Beta Demo Splunk Log Solutions Splunk BMITC CO LTD Mint Security Splunk Delivery Models Blogs
Splunk Log Format Example
 Splunk Log Format Example
https://www.splunk.com/content/dam/splunk2/en_us/screenshots/observability-cloud/splunk-log-observer-marketecture-diagram.jpg
Feb 1 2023 nbsp 0183 32 I have two fields application and servletName I d like to have them as column names in a chart I m currently trying to use eval to make a new variable named fullName and
Pre-crafted templates use a time-saving option for creating a diverse variety of files and files. These pre-designed formats and designs can be used for various personal and professional tasks, including resumes, invites, leaflets, newsletters, reports, discussions, and more, simplifying the content creation procedure.
Splunk Log Format Example
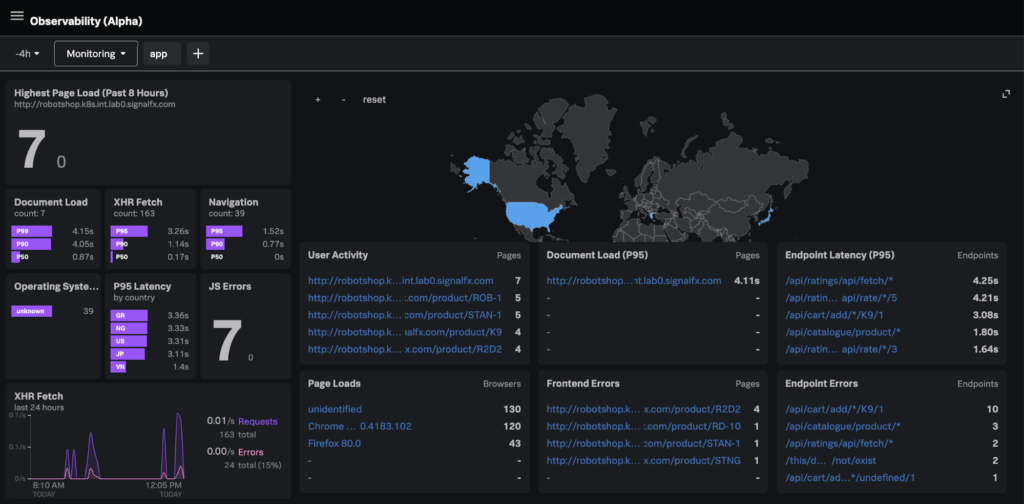
Splunk Veut Red finir L observabilit L INFORMATICIEN L INFO CYBER

Splunk Operational Intelligence InfoGuard
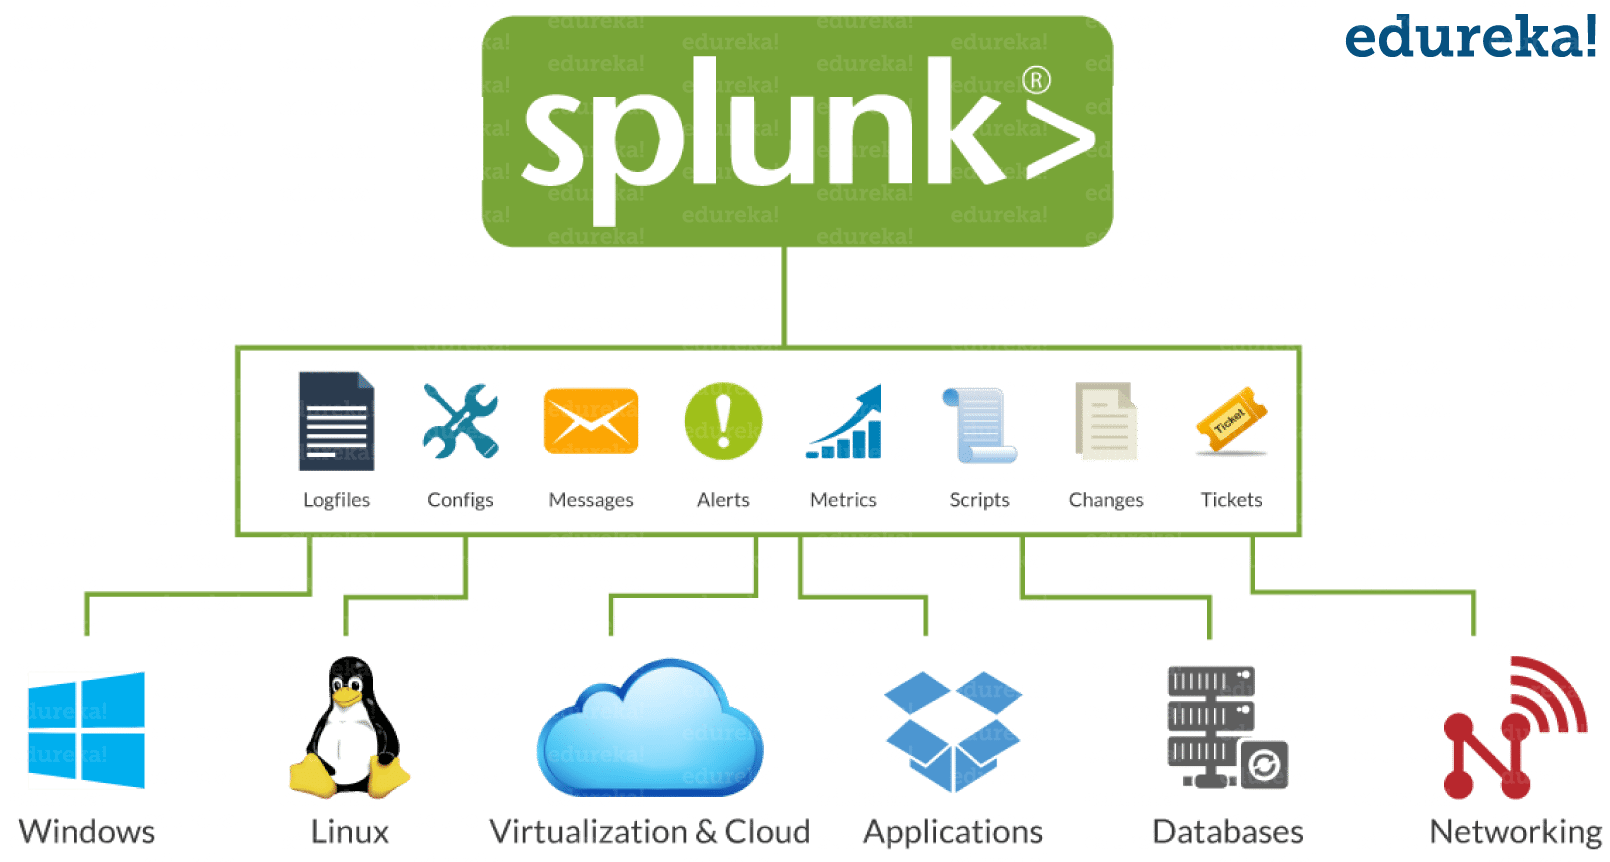
Splunk Boss Of The SOC X y D ng Gi i Ph p Thu Th p Log Cho M t Doanh

Why Should You Use Splunk For Log Analysis TO THE NEW Blog

Log Management Tools Face Off Splunk Vs Logstash Vs Sumo Logic

Splunk Log Observer Beta Demo Splunk

Jan 7 2025 nbsp 0183 32 The Splunk platform will transition to OpenSSL version 3 in a future release Actions are required to prepare for this change What s changing

Jul 23 2025 nbsp 0183 32 What s New We are excited to announce the latest enhancements to Splunk Observability Cloud as well as what is currently in preview for the Splunk Observability

Jul 16 2025 nbsp 0183 32 Are you a member of the Splunk Community Sign in or Register with your Splunk account to get your questions answered access valuable resources and connect with experts

Nov 29 2019 nbsp 0183 32 Hello I did some reading up on the hot warm and cold buckets and data retention of indexes but I am not sure I 100 get it What I am simply trying to do is to set my indexes to
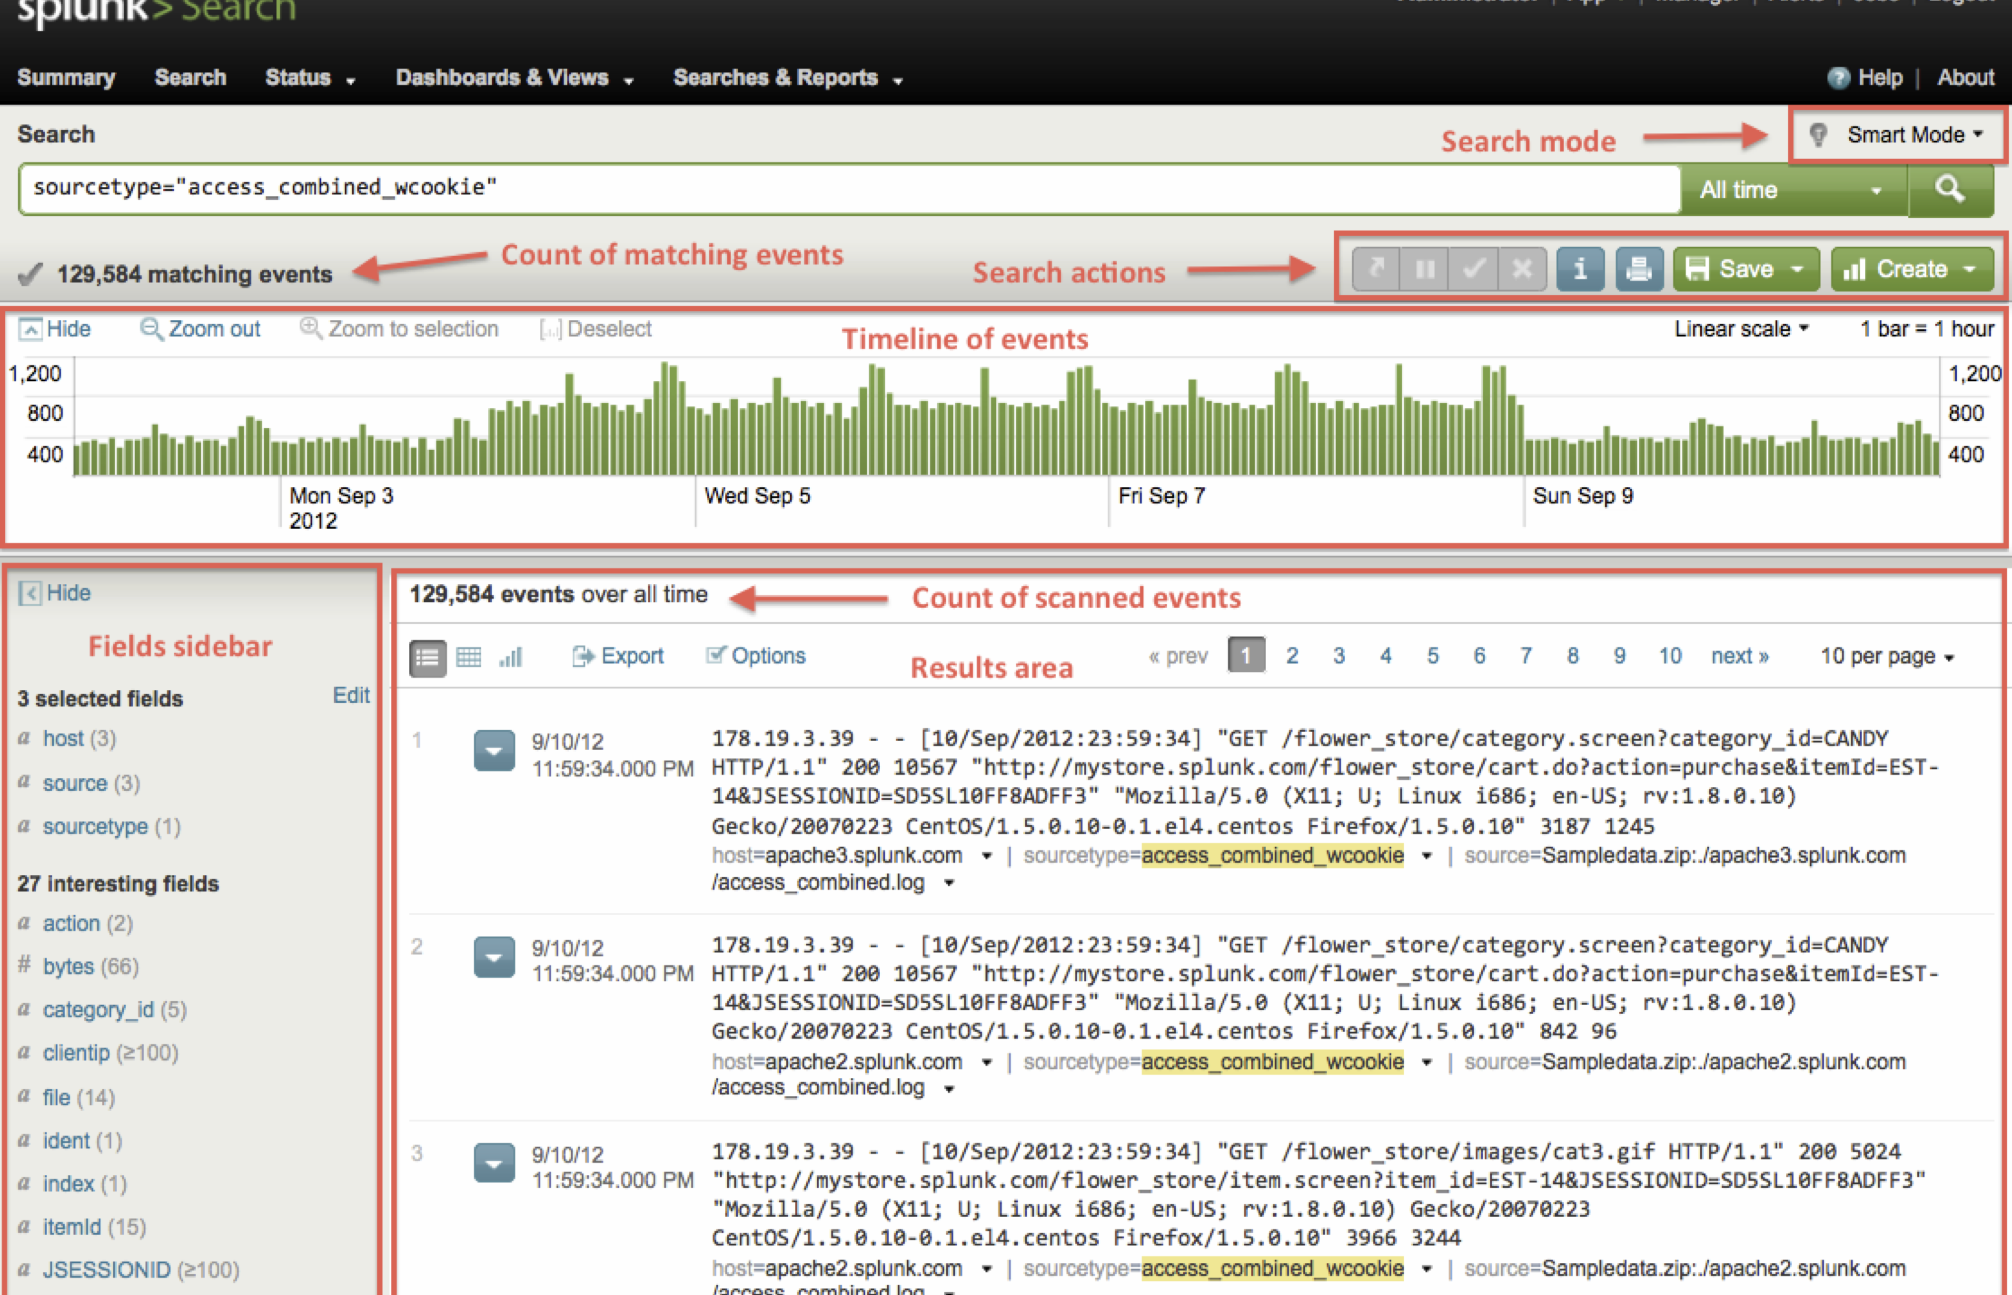
Dec 16 2024 nbsp 0183 32 Hey Splunky People We are excited to share the latest updates in Splunk Enterprise 9 4 In this release we have many awaited features and enhancements for both
[desc-11] [desc-12]
[desc-13]