Splunk Log Analysis Example Using Splunk For SEO Log File Analysis Splunk Let S Search The Data Using Splunk Crest Data Systems Gambaran Cost Of Splunk Greekpowen Windows Event Logs Analysis Splunkbase Splunk Log Observer Splunk With Splunk Log Observer you can collect index and search log data in real time and use powerful analysis and visualization tools to identify patterns trends and anomalies You can also use it to create custom dashboards and alerts to help you monitor the health and performance of
Jul 25 2024 nbsp 0183 32 Audit Logs capture who did what where and when They are primarily used for compliance security and computer forensic investigations Audit logs track user actions and system changes to ensure accountability and traceability They provide a chronological record of activities crucial for audits and compliance checks Work with your development team to establish detailed organized human readable logs Encourage development teams to create tags and notations in logs for easier identification Include creating custom reports dashboards and alerts in each application backlog Build analytics to support all code as part of its delivery criteria before
Splunk Log Observer Splunk Getting Started With Splunk Basic Searching Data Viz Stratosphere IPS Splunk mission control dashboard Login AS Splunk Web Server Log Analysis UnBrick ID Top Data Analytics Tool Splunk Dashboard Zsah Windows Event Logs Analysis Splunkbase Using Splunk For SEO Log File Analysis Splunk Splunk Log Analytics Available In Lower cost Light Version InfoWorld 3 Useful Tools For Big Data Log Analysis Big Data Analytics News
Splunk Log Analysis Example
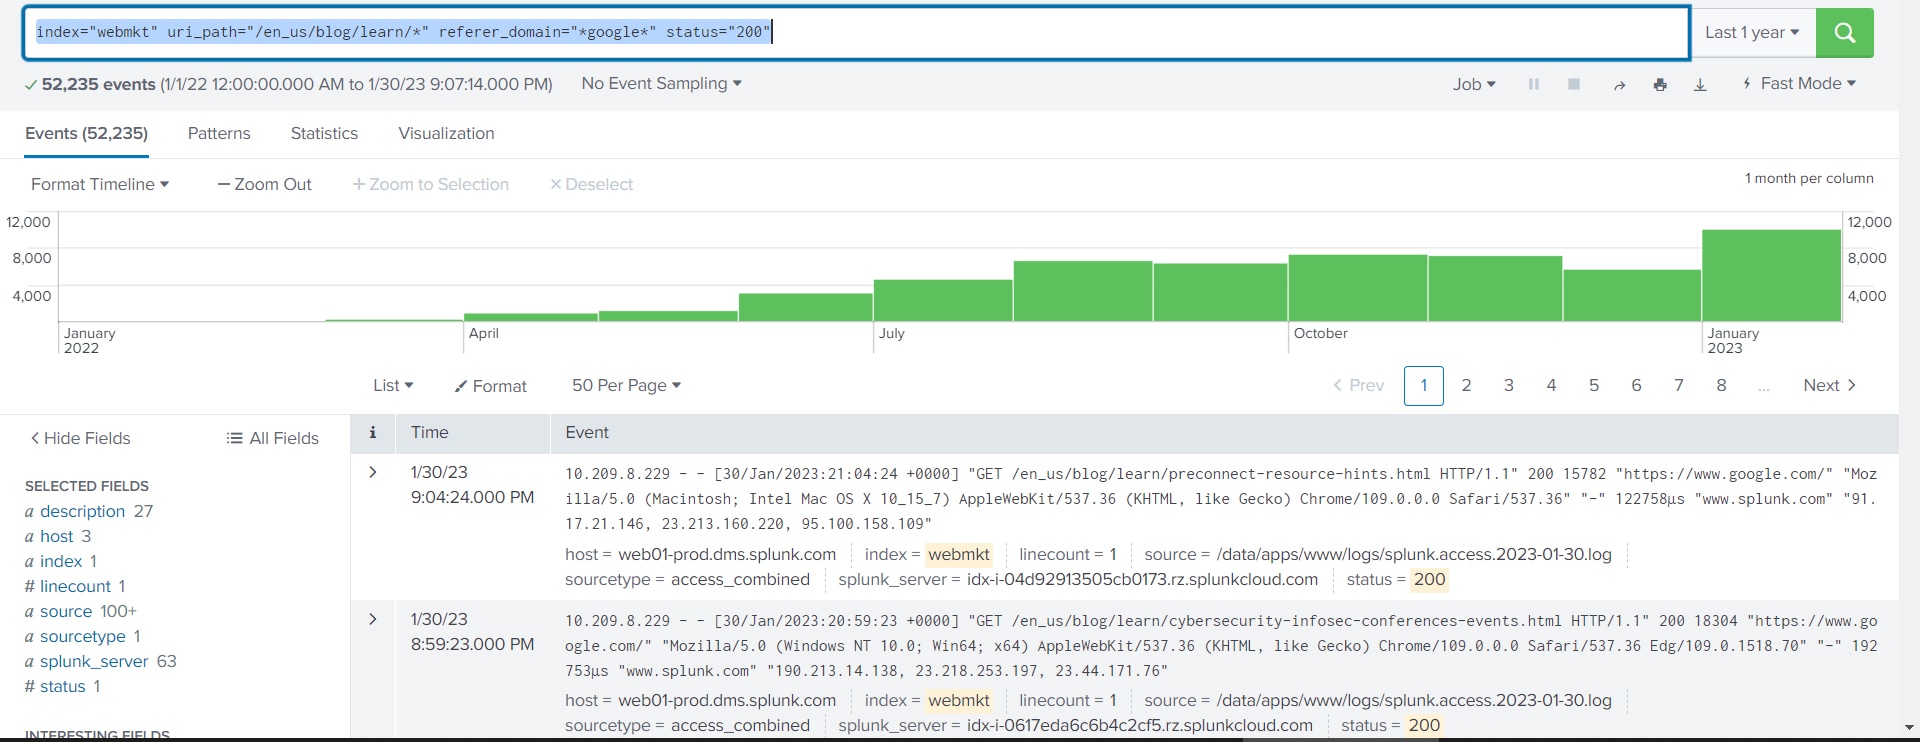 Splunk Log Analysis Example
https://www.splunk.com/content/dam/splunk-blogs/images/en_us/2023/01/blog-learn-site-entries-splk.jpg
Apr 17 2024 nbsp 0183 32 Examples of machine data include system logs web server logs application logs and sensor data from IoT devices This is the actual source of information we need to ingest into any data analytical tool to get the desired output or answers to our questions
Pre-crafted templates provide a time-saving solution for creating a diverse series of files and files. These pre-designed formats and layouts can be made use of for various personal and professional projects, consisting of resumes, invitations, flyers, newsletters, reports, discussions, and more, streamlining the content creation procedure.
Splunk Log Analysis Example
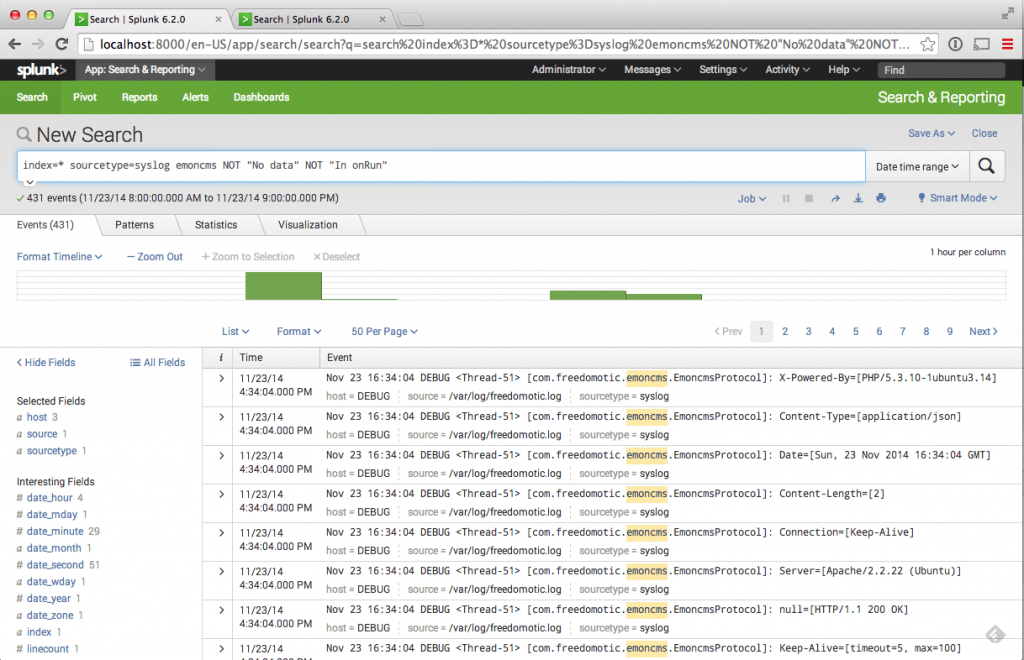
TOP Ubiquiti logs splunk
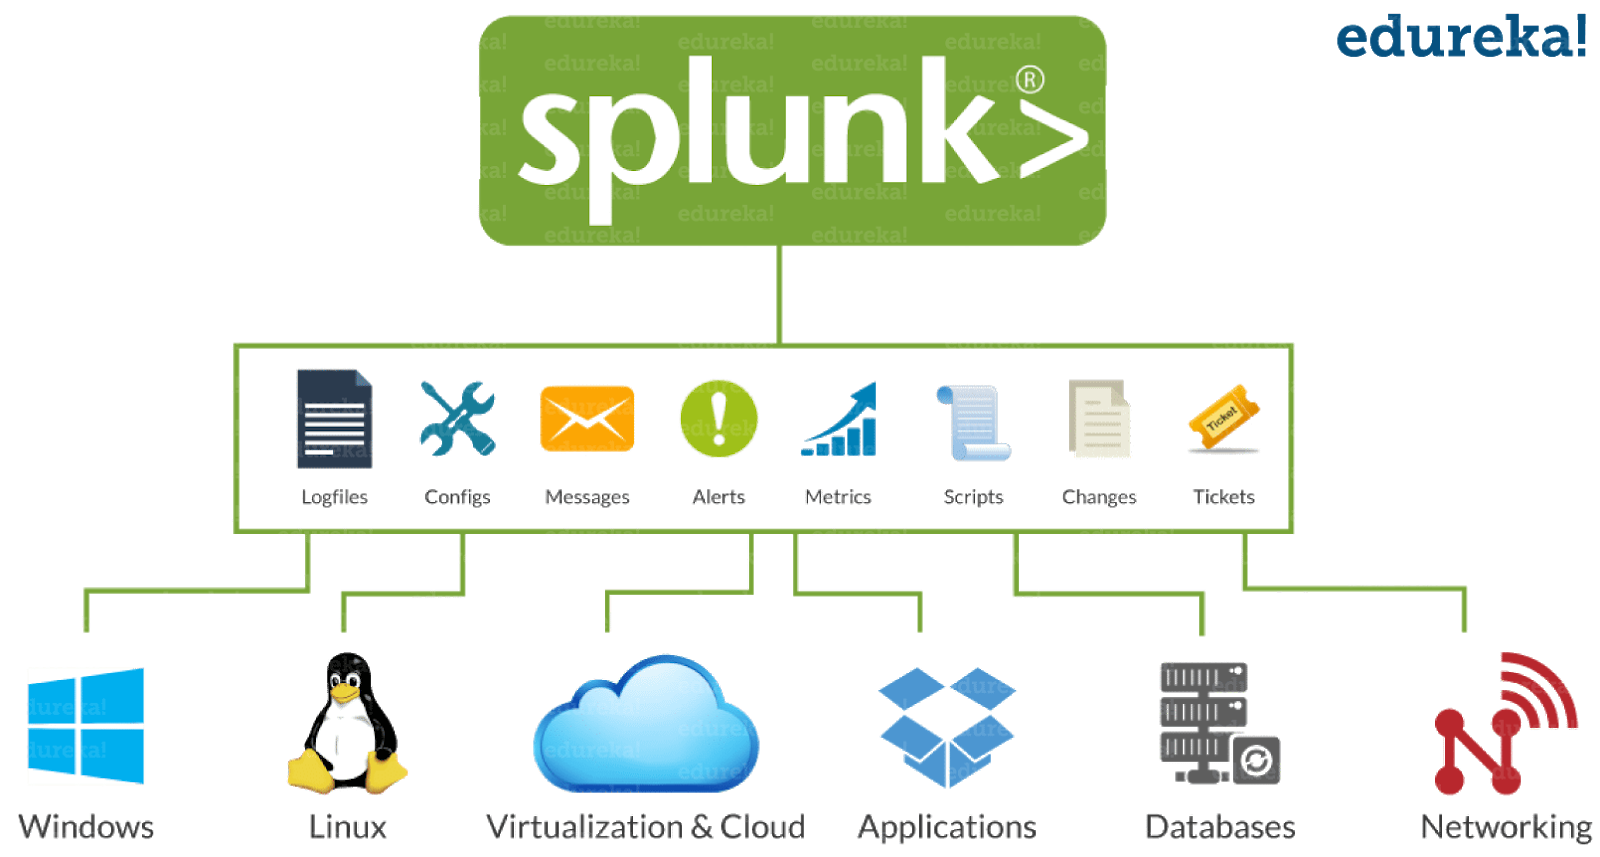
Getting Started With Splunk Basic Searching Data Viz Stratosphere IPS
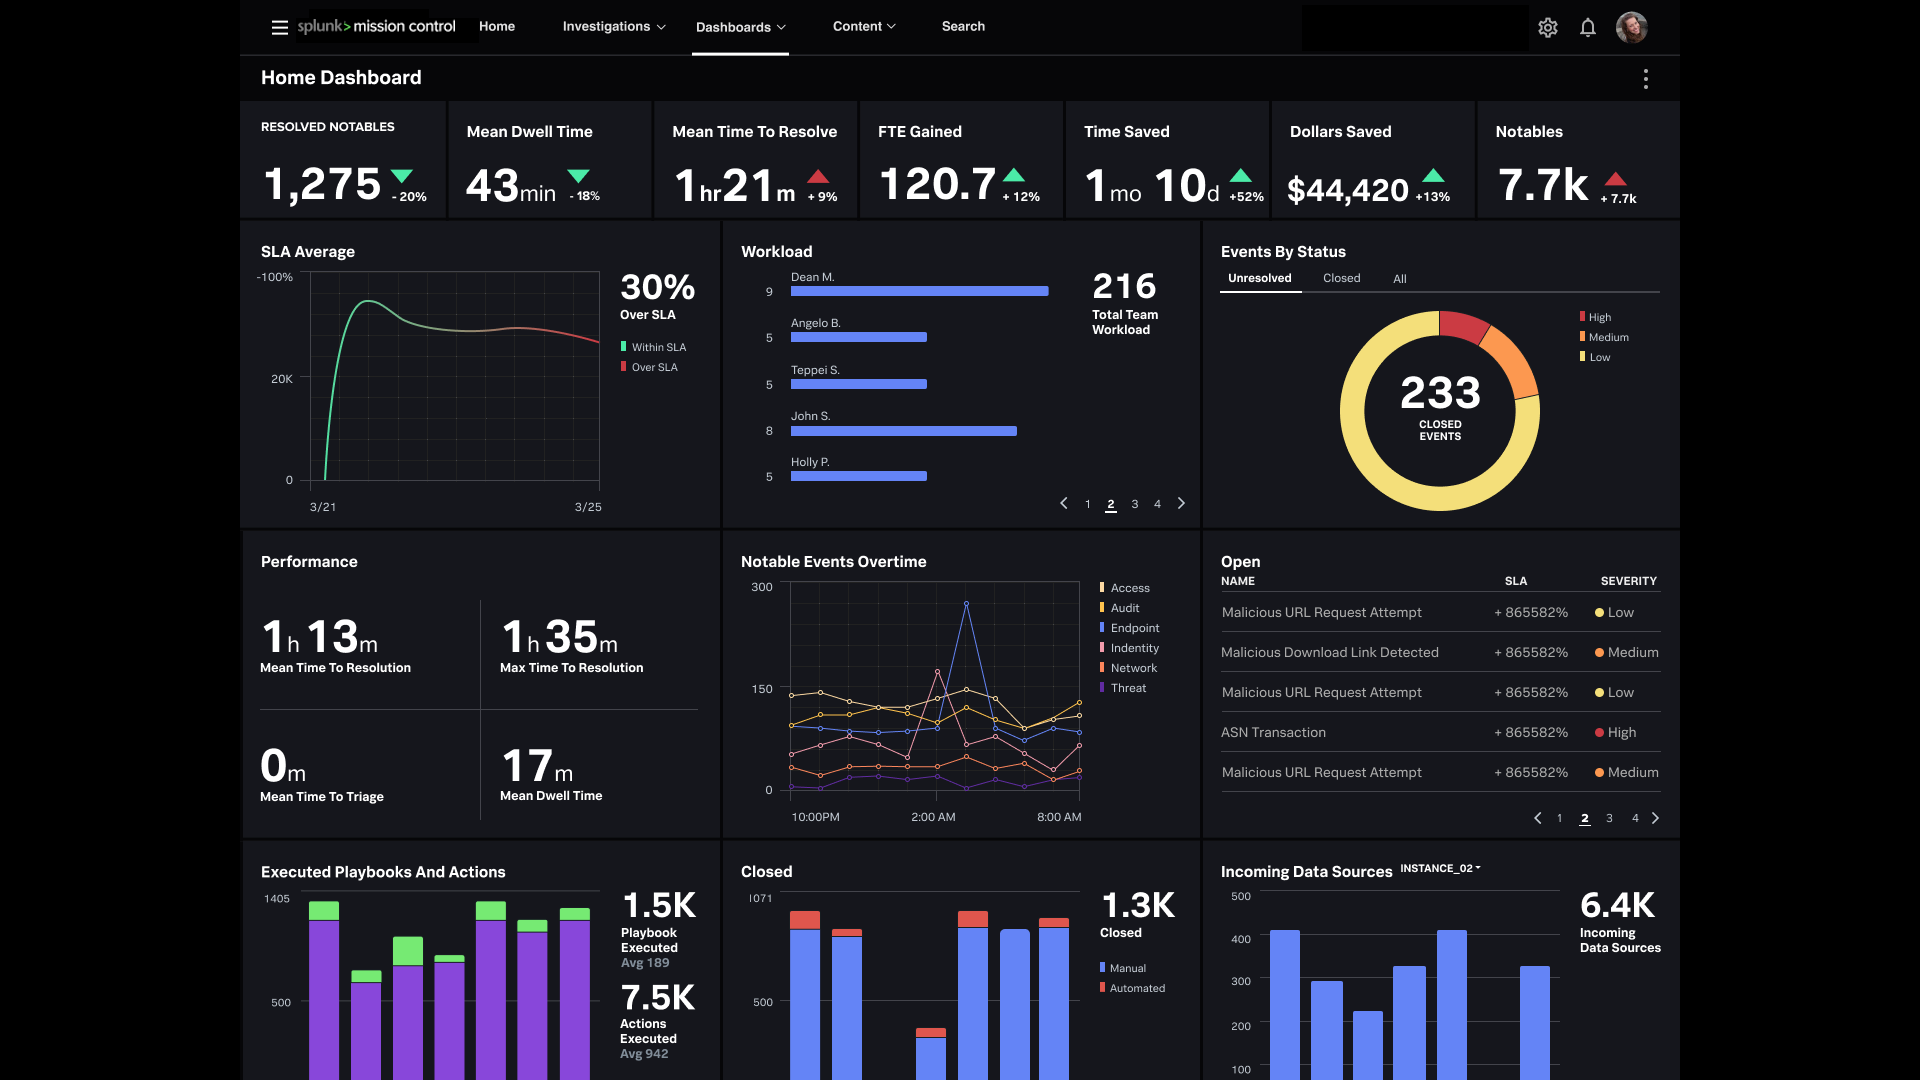
Splunk mission control dashboard Login AS

Splunk Web Server Log Analysis UnBrick ID

Windows Event Logs Analysis Splunkbase
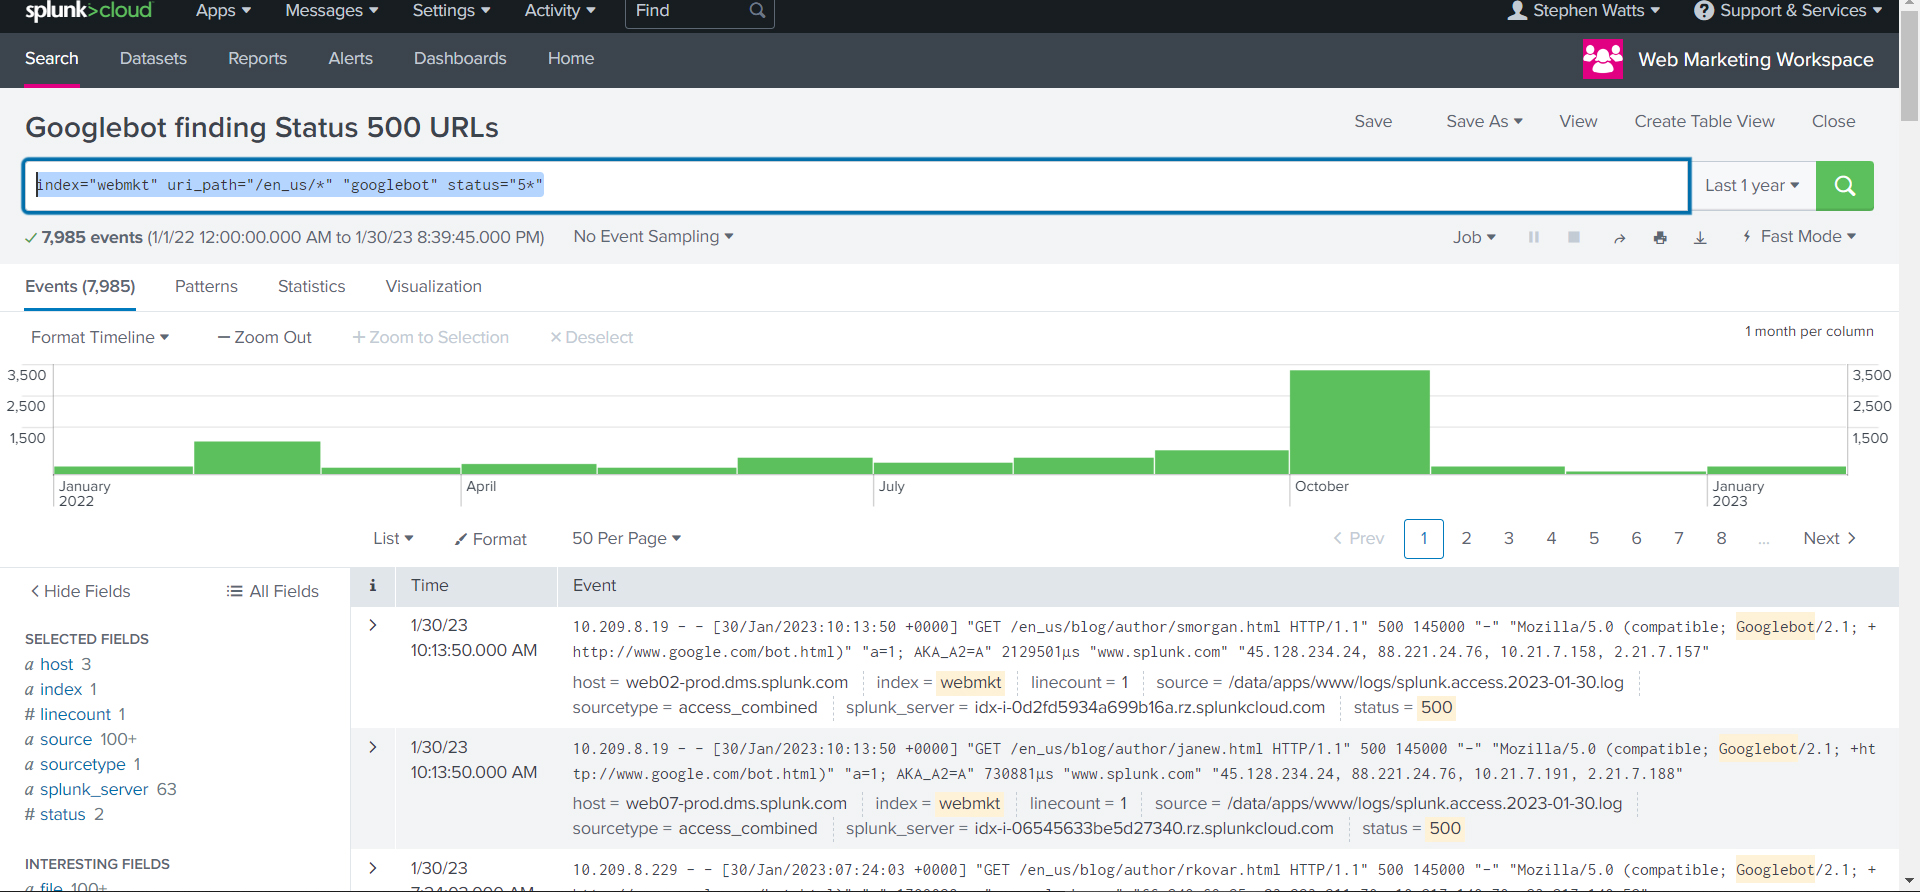
Using Splunk For SEO Log File Analysis Splunk

Dec 13 2023 nbsp 0183 32 Organizations can use log management tools to monitor logs in real time alerting them to any potential issues or security breaches Analysis Once collected parsed and stored the next step is to analyze the log data for system performance monitoring troubleshooting or security purposes Reporting

Splunk Training amp Certification https www edureka co splunk certification trainingThis

Jun 27 2024 nbsp 0183 32 Whether you re just starting out or looking to enhance your skills this blog will provide the insights and knowledge you need to effectively use Splunk for log analysis in cybersecurity Let s dive in and explore how to turn data into actionable insights with Splunk

Jun 10 2024 nbsp 0183 32 In this article A Beginner s Guide to Splunk Logs we will list the primary logs for Splunk Enterprise and where to find them We ll also provide advice on when to use the logs directly and when to use search

Nov 13 2023 nbsp 0183 32 A key aspect of incident response process is log analysis Log analysis can be deployed to detect suspicious activities in an organization s network domain or hardware
L A M E Log Analysis Made Easy Training app is a splunk app that focuses on training analysts how to use the SPL language and many of the features within Splunk such as saved searched dashboards datamodels and the SPL query language Feb 22 2018 nbsp 0183 32 1 Eventgen App on Splunkbase This app can be used to generate dyummy data live based on sample data added to the app Refer to youtube walk thru from Clint Sharp 5 min video on setting up the App and how to use it
Feb 5 2024 nbsp 0183 32 While Log Observer visual analysis allows you to dynamically view aggregate metrics in the context of your query log metricization rules allow you to embed metrics from log data in charts dashboards and detectors