Splunk Json Log Example Splunk On LinkedIn Splunk Enterprise Security Splunk JSON Structured Data The SEDCMD In Splunk TekStream Solutions Splunk mission control dashboard Login AS Splunk Configuration File Precedence SOC Library Splunk License Estimations Kinney Group WEB Extract JSON fields from data using Ingest Processor You can create a pipeline that extracts JSON fields from data Field extraction lets you capture information from your data in a more visible way and configure further data processing based on those fields
WEB Sep 5 2018 nbsp 0183 32 For extracting the fields from the json format data we will use one command called spath We will run the below query and all the fields from the Splunk Json Data will be extracted like magic QUERY index json sourcetype jsonlog spath input message Explanation WEB Put semantic meaning in events to get more out of your data Log audit trails what users are doing transactions timing information and so on Log anything that can add value when aggregated charted or further analyzed In other words log anything that is interesting to the business
Splunk License Estimations Kinney Group Getting Started With Splunk Basic Searching Data Viz Stratosphere IPS Splunk Platform Upgrade Readiness App Warning On Splunklib Py Files JSON Dateien In R R Coding Forwarding Pretty JSON Logs To Splunk How To Extract A Field From A JSON Object In PostgreSQL Mission Possible Splunk Observability Adoption Challenge Splunk Splunk Forwarder Login Failed logging Remove JSON Formatted log Line After Parsing JSON Fields
Splunk Json Log Example

https://media.licdn.com/dms/image/D4E18AQEhqOjZlr5W4Q/companyUpdate-article-image-shrink_1280/0/1651642213986/22-23793-Splunk-AwarenessAdCampaign-Security-V1-107_1080x1080jpg?e=2147483647&v=beta&t=oj03NDjWA2oRsiAl5q_DLLQT3aksRtLIAH2V76Wn2lw
WEB 1 Identify a JSON value This example shows how you can use the json function to confirm that a value is JSON The following search verifies that quot animal quot quot pony quot is a JSON value by returning its value quot animal quot quot pony quot eval animals json object quot animal quot quot pony quot result json animals
Templates are pre-designed documents or files that can be used for various purposes. They can conserve time and effort by supplying a ready-made format and design for developing different kinds of material. Templates can be utilized for individual or expert jobs, such as resumes, invitations, leaflets, newsletters, reports, discussions, and more.
Splunk Json Log Example
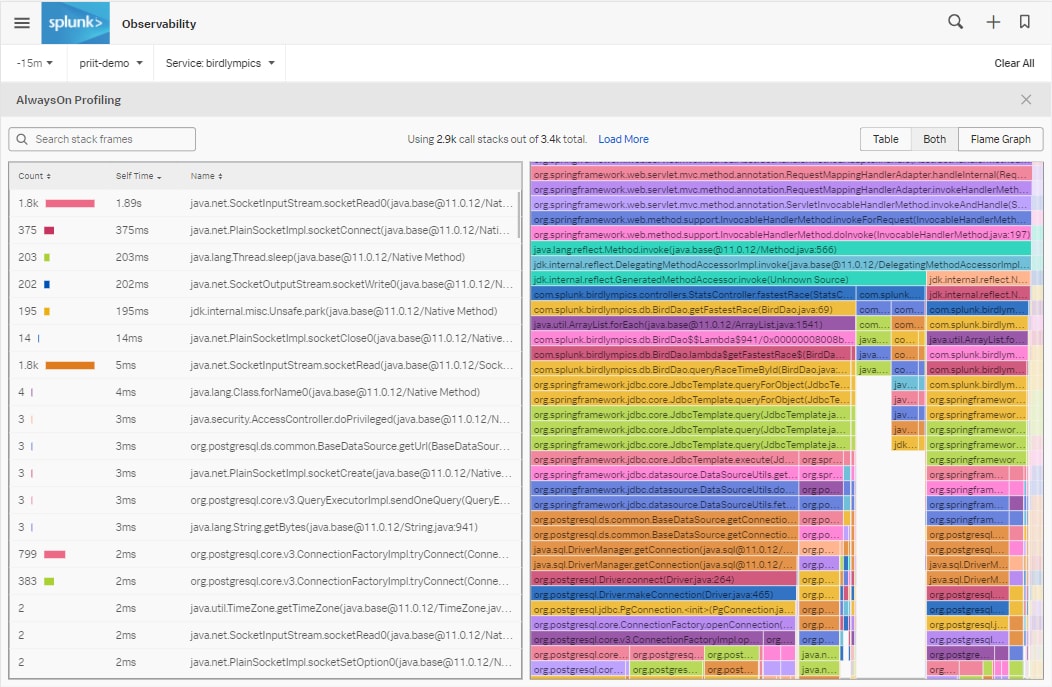
Announcing The Preview Of Splunk APM s AlwaysOn Profiling Splunk
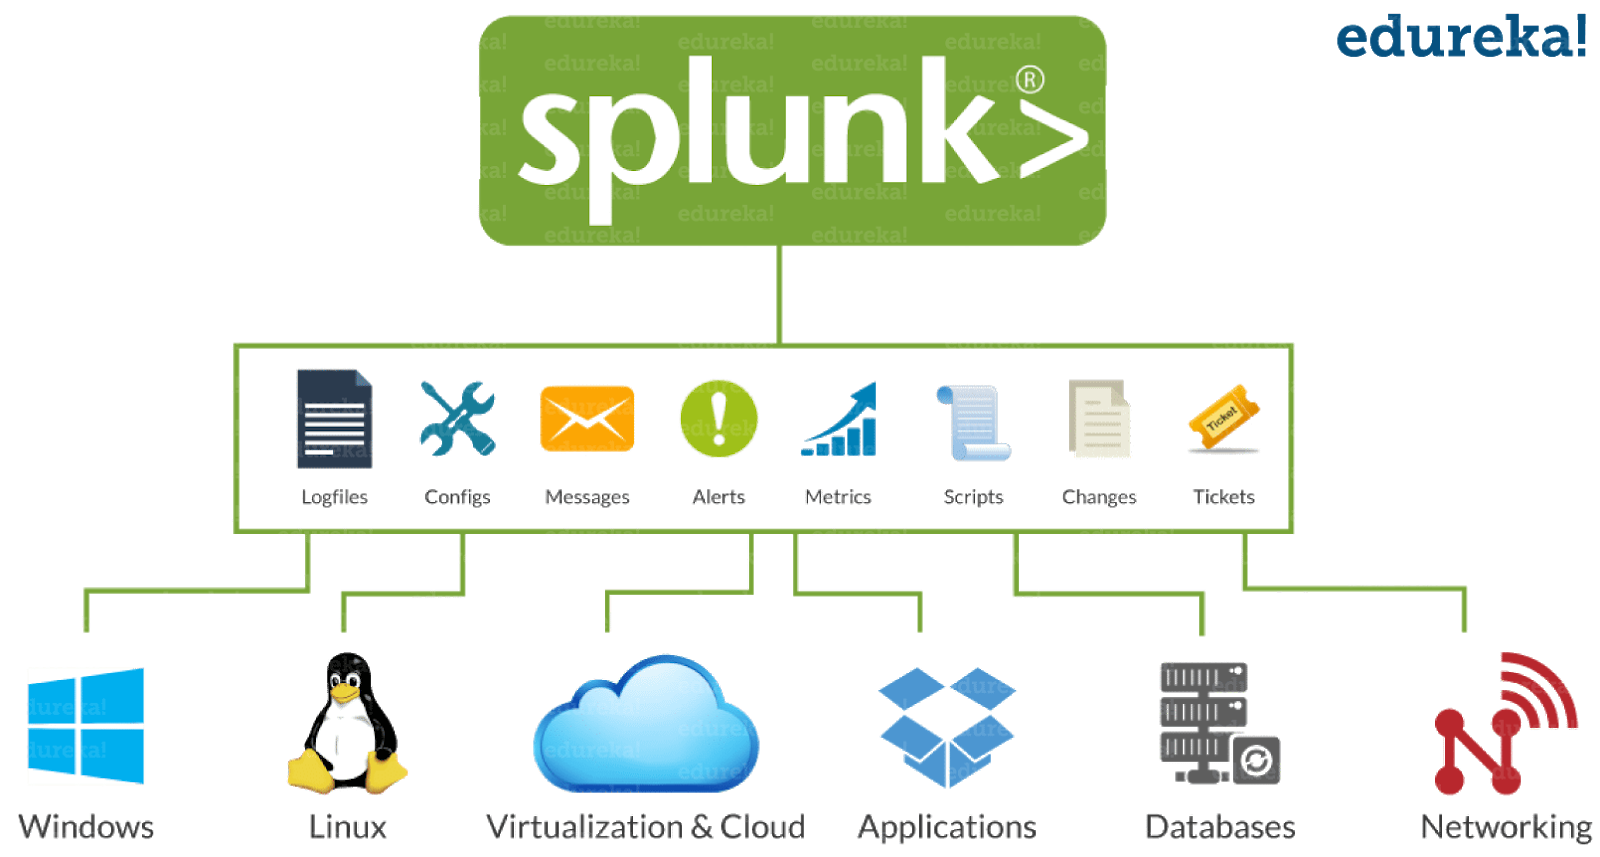
Getting Started With Splunk Basic Searching Data Viz Stratosphere IPS

Splunk Platform Upgrade Readiness App Warning On Splunklib Py Files
JSON Dateien In R R Coding
How To Extract A Field From A JSON Object In PostgreSQL

Mission Possible Splunk Observability Adoption Challenge Splunk

WEB Jan 3 2014 nbsp 0183 32 The log file contains JSON data which is the bread butter for splunk This is a mixed data whereby the logging application puts some info like logging time messageSeverity class thread etc Later the JSON message starts like json

WEB Jul 13 2018 nbsp 0183 32 Splunk does the auto json formatting for the field raw on Events tab update raw to just have the pure json content worked here If there are no follow up questions to this please close this question by accepting this answer

WEB Examples These examples show different ways to use the json object function to create JSON objects in your events 1 Create a basic JSON object The following example creates a basic JSON object quot name quot quot maria quot eval name json object quot name quot quot maria quot 2 Create a JSON object using a multivalue field

WEB Sep 10 2020 nbsp 0183 32 I have a log event getting in a json format like this quot level quot quot level name quot quot exception quot quot exception message quot quot logger quot quot com log amp quo

WEB Dec 13 2023 nbsp 0183 32 Log management example key pairs To help you understand how log management works let s walk through an example for key pairs Let s take string format for our log example In this example the data is about
WEB May 8 2021 nbsp 0183 32 You could have a log structure defined using pattern or you could publish in JSON format JSON is beneficial as you can query on attributes in Splunk and that in turn is helpful for making WEB Example walkthrough Splunk logging for NET can send JSON objects directly to HTTP Event Collector using Splunk Logging Common In contrast trace listeners such as those provided in Splunk Logging TraceListener and event sinks such as those provided in Splunk Logging SLAB are designed to send strings only
WEB Jul 3 2019 nbsp 0183 32 I have a splunk log where the log will be in JSON format or as raw data Need to write a splunk query using stats command index application name abc type imp stats count by status