Keycloak Saml Logout Example SAML Based Security For OData Using KeyCloak GitBook Enabling SAML Single Logout For Okta Enabling SAML Single Logout For Okta The Challenge Of Building SAML Single Logout Official Products Change Redirect uri When Logout From Keycloak Account Page Stack Overflow Web Viewed 4k times 2 I have one SP and one IDP using Keycloak I m using SAML protocol and I can successfully login and logout when the request is initiated by the SP But when connected as an admin in Keycloak I logout an user from his session no request are sent to the SP The session is indeed terminated on the IDP side but not on the SP side
Web Aug 3 2020 nbsp 0183 32 I have problem with Keycloak s configuration and Single Logout from SAML Identity Provider Scenario User tries to log into Service Provider using Keycloak s client OID KC redirects to SAML identity provider Entering correct credentials user is logged in KC creates session and user is redirected back to SP page Web Oct 11 2017 nbsp 0183 32 63 I have issue while calling Keycloak s logout endpoint from an mobile application This scenario is supported as stated in its documentation realms realm name protocol openid connect logout The logout endpoint
Change Redirect uri When Logout From Keycloak Account Page Stack Overflow KeyCloak SAML Example Enterprise Documentation KeyCloak SAML Example Anchore Enterprise Product Documentation How To Implement Single Sign out In Keycloak With Spring Boot Red Hat Saml SAML2 Single Logout Where To Post Responses To Stack Overflow Handling SAML Single Logout Requests From Federated Identity Providers Keycloak Using React User Can Login But When I Try Logout I Get A SAML Single Logout Through OKTA Stack Overflow Zabbix Authentification SAML Avec Keycloak Et Provider Google Auth
Keycloak Saml Logout Example
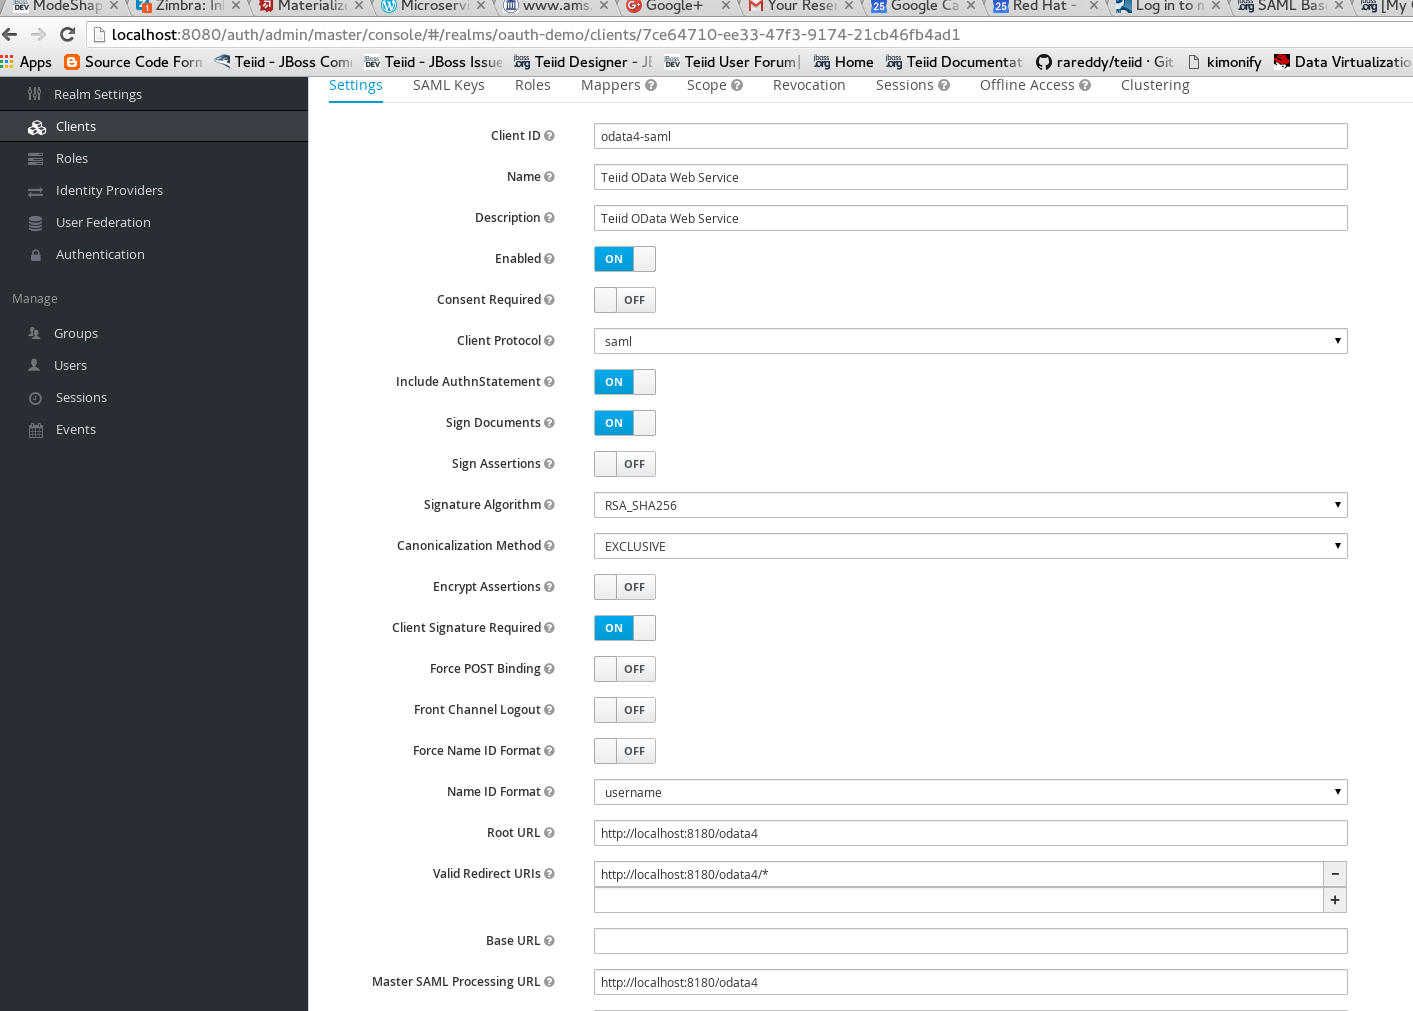 Keycloak Saml Logout Example
https://teiid.github.io/teiid-documents/master/content/security/images/saml-main.png
Web May 9 2016 nbsp 0183 32 I wanted to ask if there is a way to logout from keycloak via a single http request I already tried to POST protocol openid connect logout or tokens logout but the result is always a ORIGIN Problem But the calling ORIGIN is configured in keycloak and the login with a request works
Pre-crafted templates use a time-saving option for creating a diverse range of files and files. These pre-designed formats and designs can be made use of for different individual and expert tasks, consisting of resumes, invites, flyers, newsletters, reports, discussions, and more, simplifying the content production procedure.
Keycloak Saml Logout Example
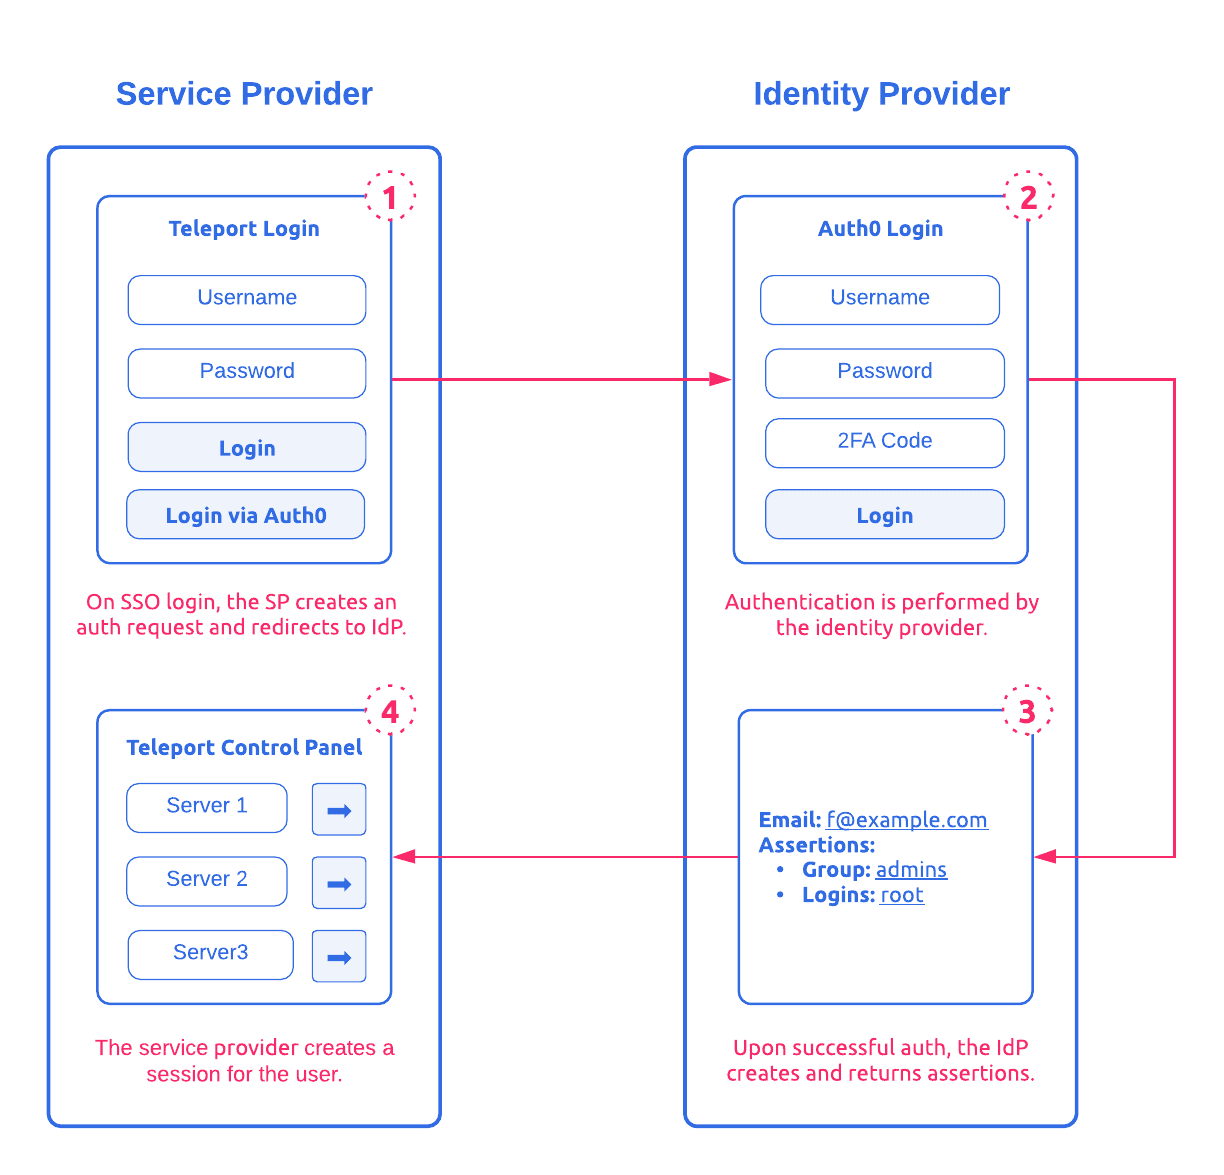
How SAML Authentication Works

KeyCloak SAML Example Enterprise Documentation

KeyCloak SAML Example Anchore Enterprise Product Documentation
How To Implement Single Sign out In Keycloak With Spring Boot Red Hat

Handling SAML Single Logout Requests From Federated Identity Providers

Keycloak Using React User Can Login But When I Try Logout I Get A

Web Feb 10 2021 nbsp 0183 32 So far what i have done is Generate the logout request payload base64 encode it url encode it and send it to the logout url as a param Assume that the realm name is Abc http auth server auth realms Abc protocol saml SAMLRequest encodedSAMLRequest The saml payload is

Web Dec 7 2022 nbsp 0183 32 Learn how to implement single sign out in Java in this demonstration of Keycloak by creating a back channel logout in Spring Boot and Keycloak Single sign on is often implemented with Keycloak Few people know that Keycloak can also implement single sign out where logging out from one application

Web Mar 3 2022 nbsp 0183 32 User session is also created in keycloak While performing logout operation the user is just logged out from my application and not from SAML The user remains active How do I perform a logout so that saml session is also cleared I found that spring saml supports quot saml logout quot to clear the session

Web Feb 4 2021 nbsp 0183 32 We have several mobile applications Android and multiple websites that all use the same Keycloak v11 server instance we setup for SSO The login part seems to be working well so far Now we want to give our users the ability to logout globally from all apps and websites allowing them to switch users

Web Securing Applications and Services Guide 1 Planning for securing applications and services As an OAuth2 OpenID Connect and SAML compliant server Keycloak can secure any application and service as long as the technology stack they are using supports any of these protocols
Web Apr 11 2022 nbsp 0183 32 Keycloak Single logout with Azure AD saml Application Microsoft Q amp A Ask a question Keycloak Single logout with Azure AD saml Application Jon 1 Apr 11 2022 3 18 PM We have configured keycloak as our identity provider and have added Azure AD as an identity provider using SAML Web Sep 24 2017 nbsp 0183 32 I m running the saml broker authentication example The first thing that I see is in the UI is a user pass for with an option to use a broker image below Is there a way to skip this form and go In keycloak admin console go to quot Authentication quot menu gt quot Flows quot panel gt in the drop down select quot Browser quot gt click on the quot copy quot button and
Web on Jan 16 2021 I m currently setting up Kimai using Keycloak as the SAML Identity Provider Login works perfectly But I can t for the life of me get a logout configuration working Here are some relevant snippets from my local yaml