Keycloak Authentication Example Keycloak authentication spi example Spring security oauth2 client for keycloak README md At Main Shinyay Authentication Authorization Flow Standard Payments Google For Sciencegateways Tech Blog Using Keycloak To Provide Authentication How To Integrate Keycloak For Authentication With Apache APISIX Keycloak Some examples are passwords one time passwords digital certificates or even fingerprints Roles identify a type or category of user Groups manage groups of users Attributes can be defined for a group You can map roles to a group as well Users that become members of a group inherit the attributes and role mappings that group defines
Implementing a function to inspect each request for a bearer token and send that token off for validation by your Keycloak server at the userinfo endpoint before it is passed to your api s route handlers Code example using Node js Express Keycloak invokes the create method for every transaction passing a KeycloakSession and a ComponentModel as arguments Here a transaction means any action that requires access to the user store The prime example is the login flow at some point Keycloak will invoke every configured user storage for a given Realm to validate a credential
How To Integrate Keycloak For Authentication With Apache APISIX Keycloak GitHub Halazv2 keycloak theme Create A Custom Theme For Keycloak Error Authentication Saml In Proxysg Snoed Keycloak Custom Authentication Flows YouTube How Do I Activate Authorization Codes Auth Codes Leia Aqui What Is LDAP Authentication With Azure Active Directory Microsoft Entra OAuth2 Authentication With API Gateway In A Distributed Environment Blog Use Keycloak With API Gateway To Secure APIs Apache APISIX Cloud How To Integrate Keycloak For Authentication With Apache APISIX Keycloak
Keycloak Authentication Example
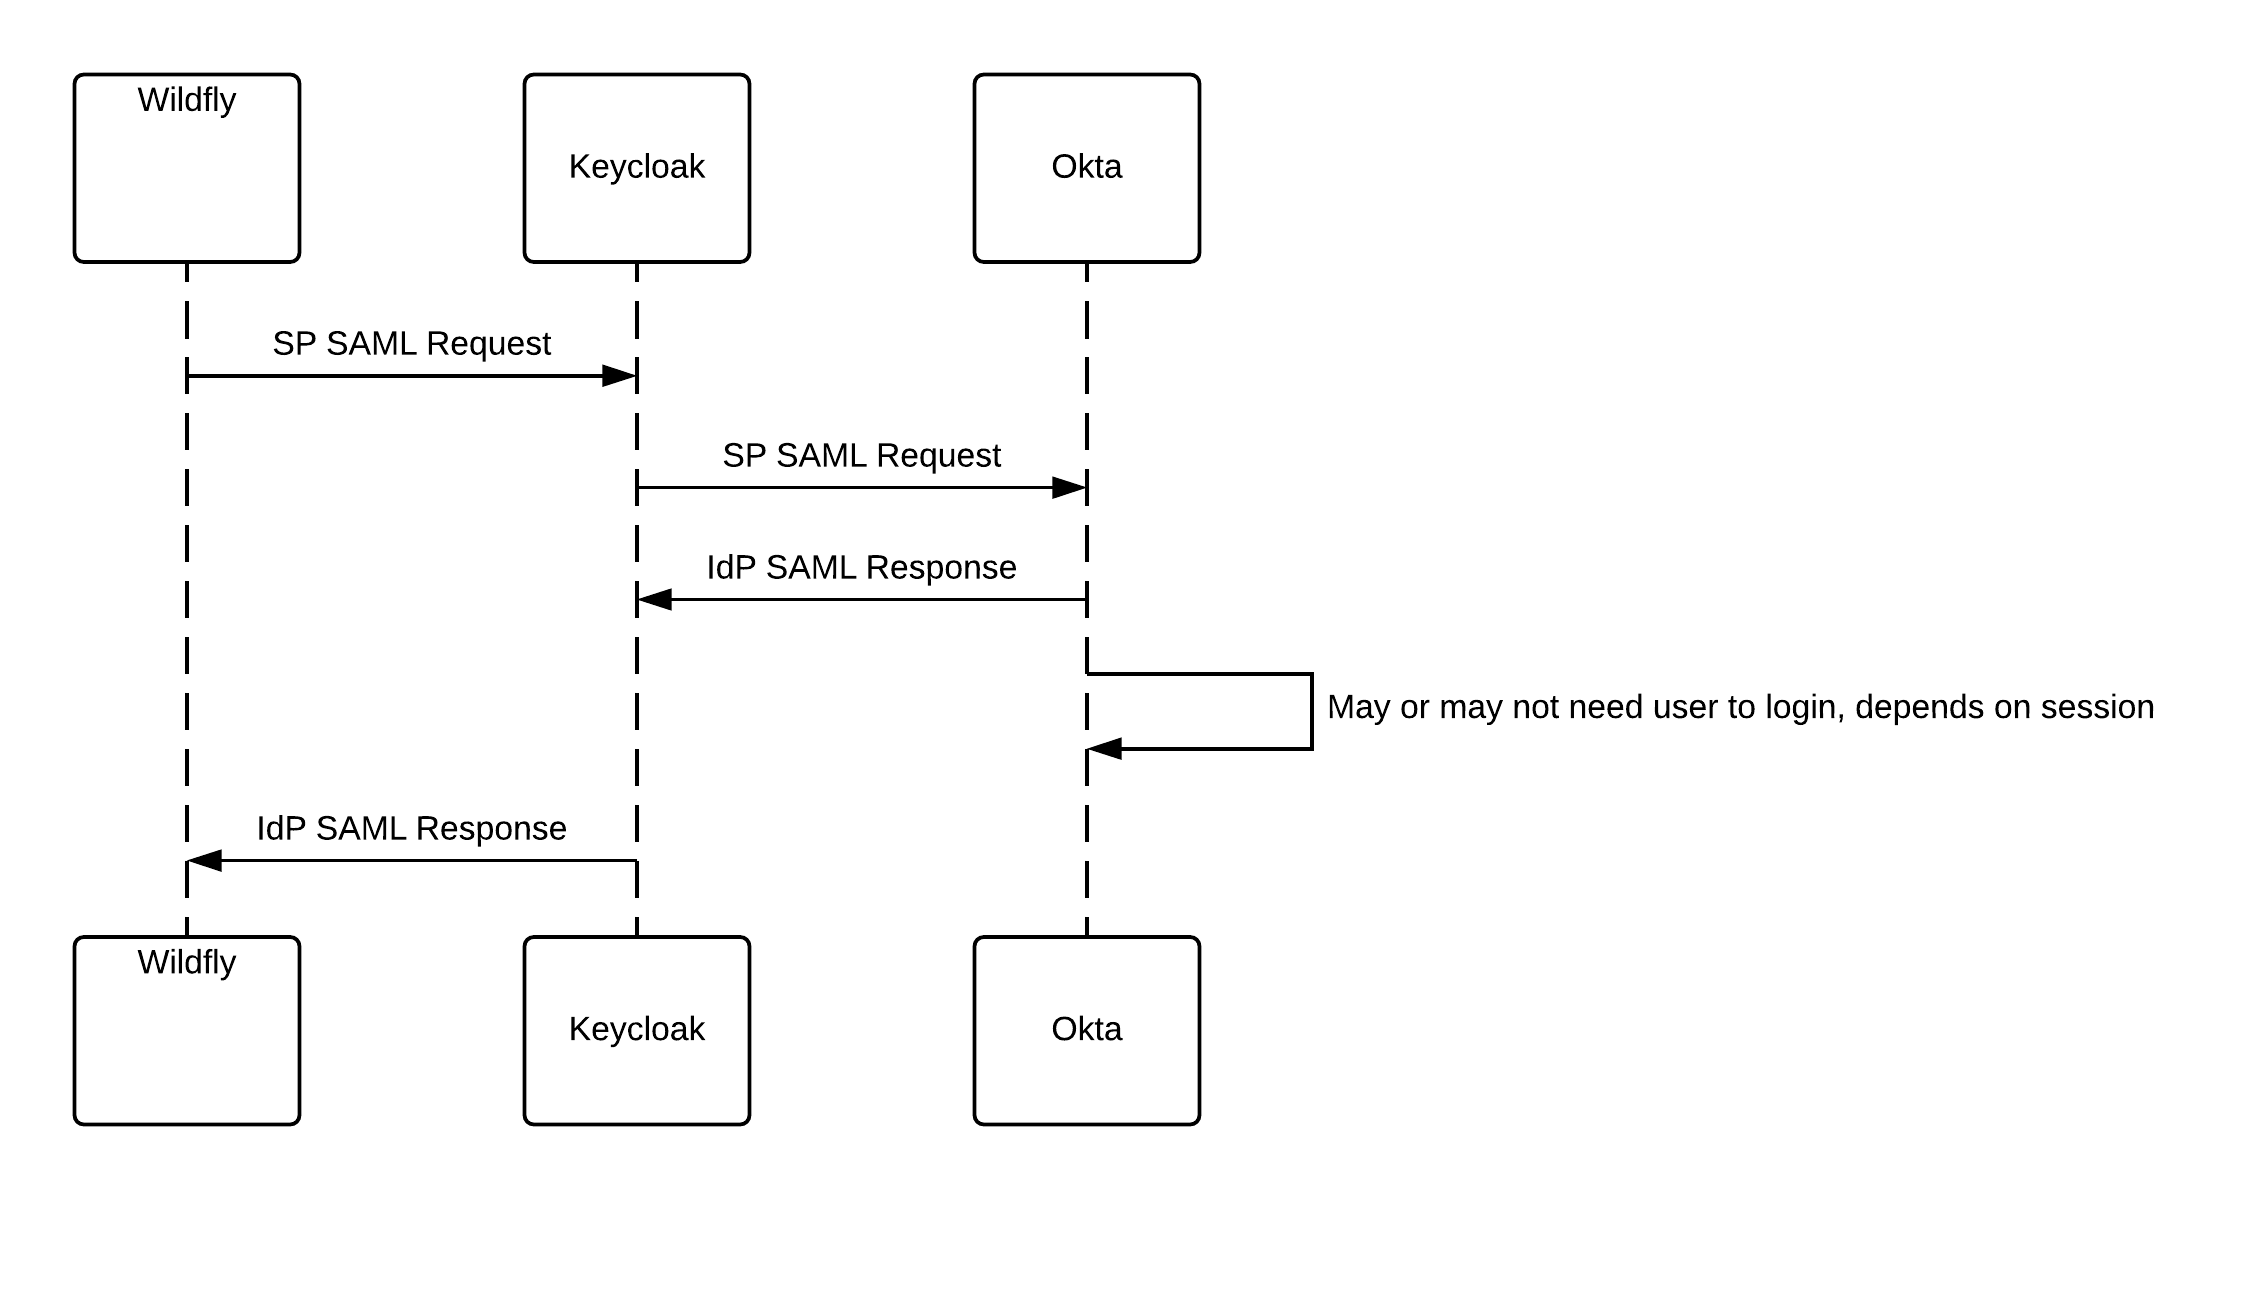 Keycloak Authentication Example
http://lists.jboss.org/pipermail/keycloak-user/attachments/20180720/30a40b8c/attachment-0001.png
1 Access Control Authentication and Authorization Managing authentication and authorization is an essential task in every well designed web application or service Keycloak makes it very easy and practical letting us focus on the application business logic rather than on the implementation of security features
Templates are pre-designed files or files that can be utilized for different functions. They can save effort and time by offering a ready-made format and layout for producing various kinds of material. Templates can be used for personal or expert tasks, such as resumes, invitations, leaflets, newsletters, reports, discussions, and more.
Keycloak Authentication Example
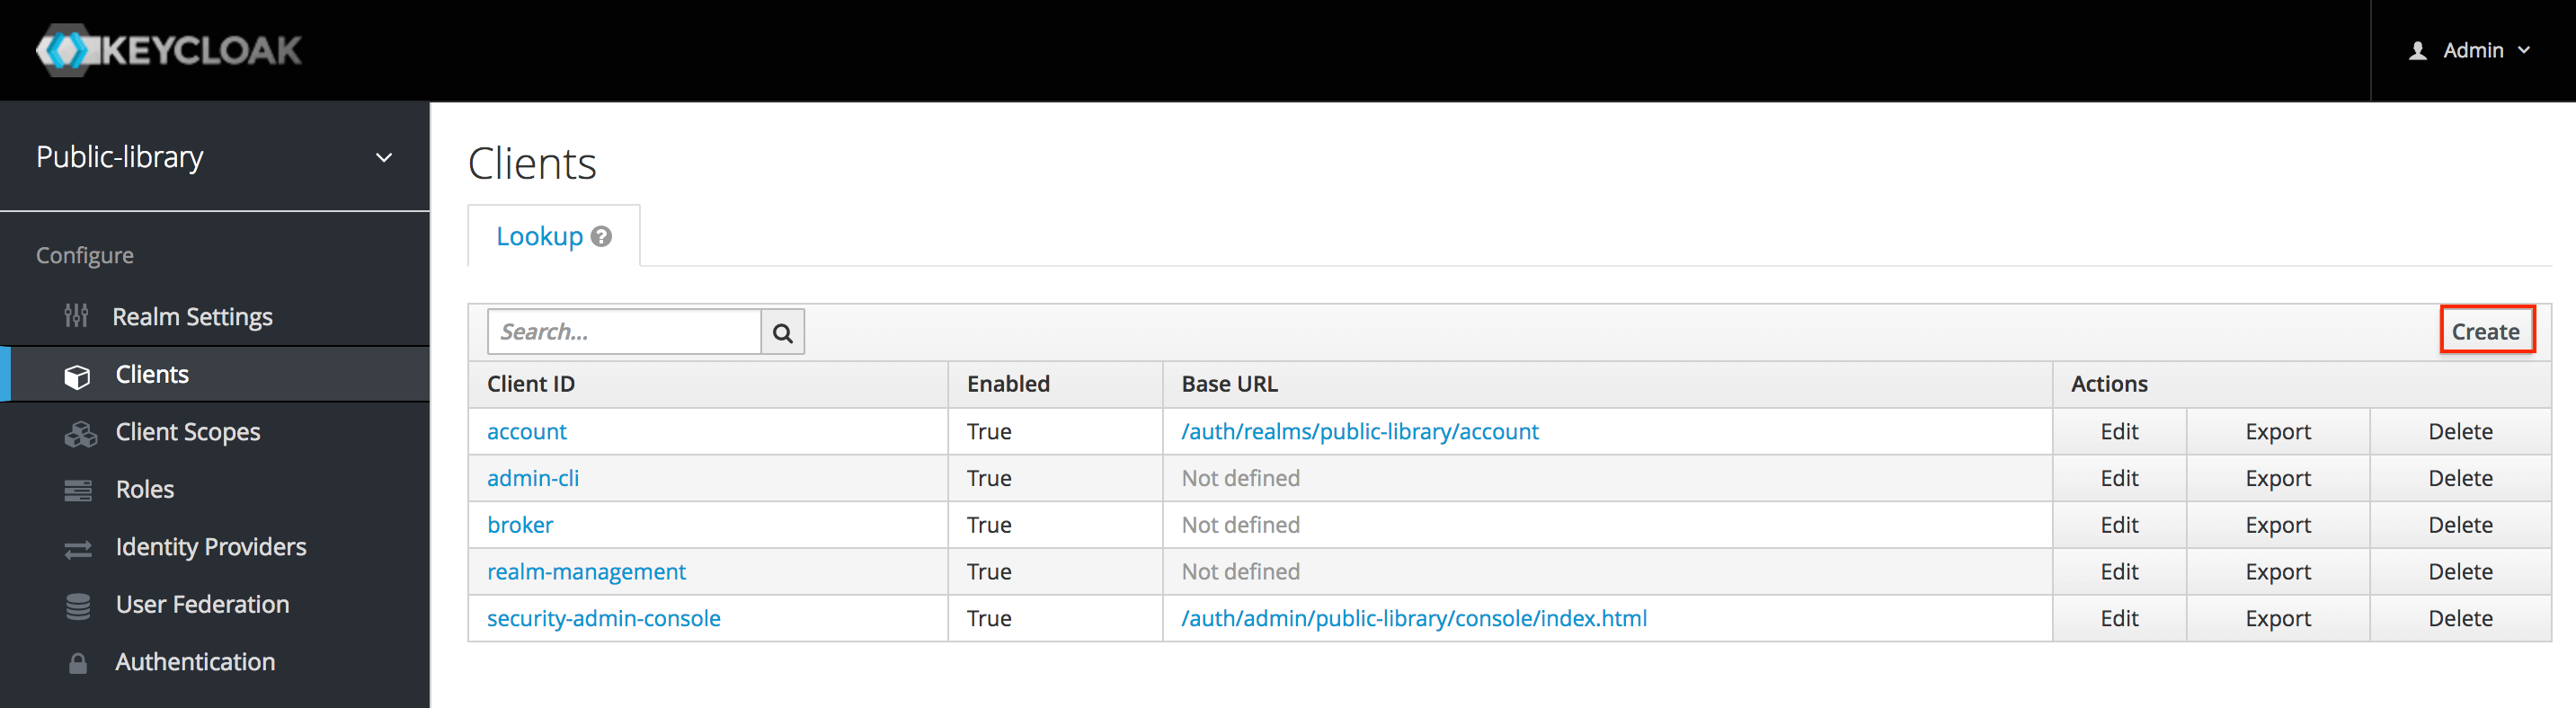
Keycloak Authentication Flows SSO Protocols And Client Configuration

GitHub Halazv2 keycloak theme Create A Custom Theme For Keycloak
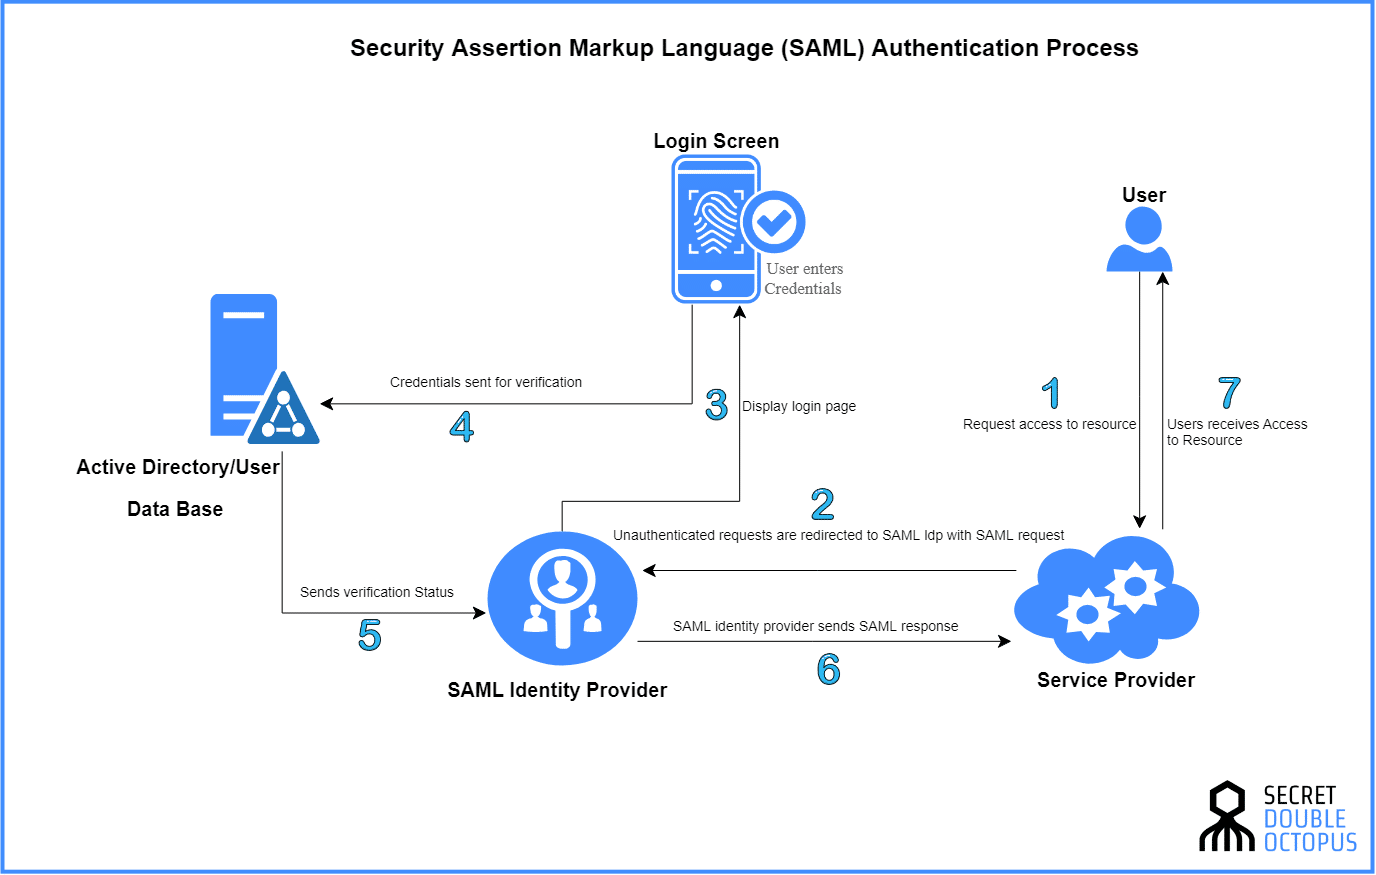
Error Authentication Saml In Proxysg Snoed

Keycloak Custom Authentication Flows YouTube
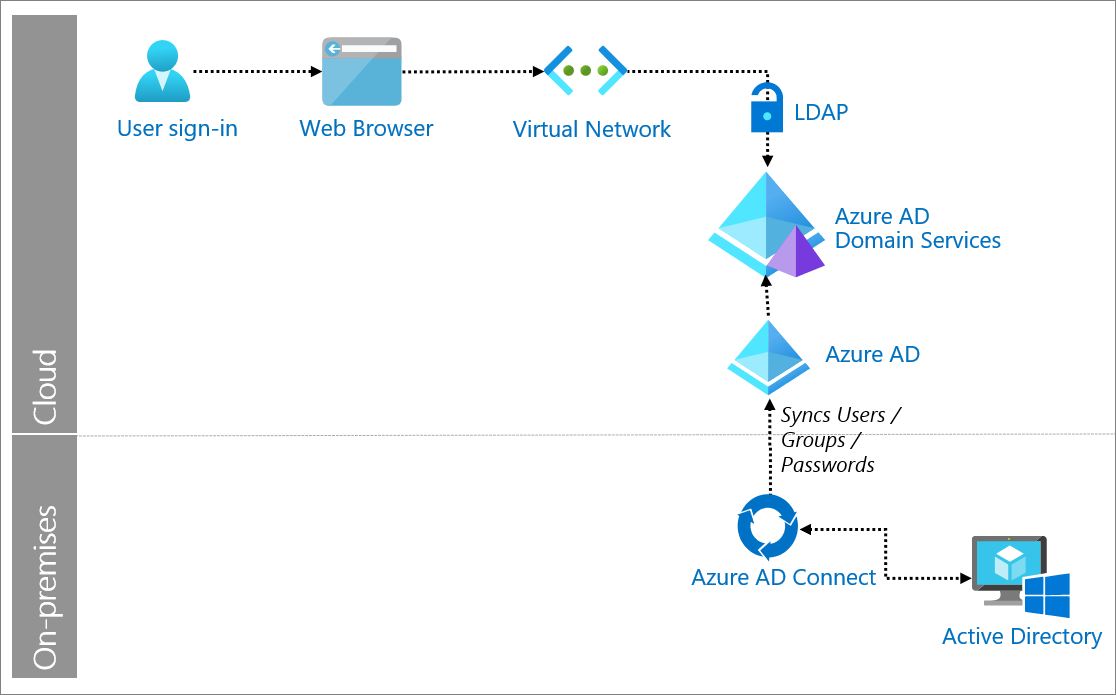
LDAP Authentication With Azure Active Directory Microsoft Entra
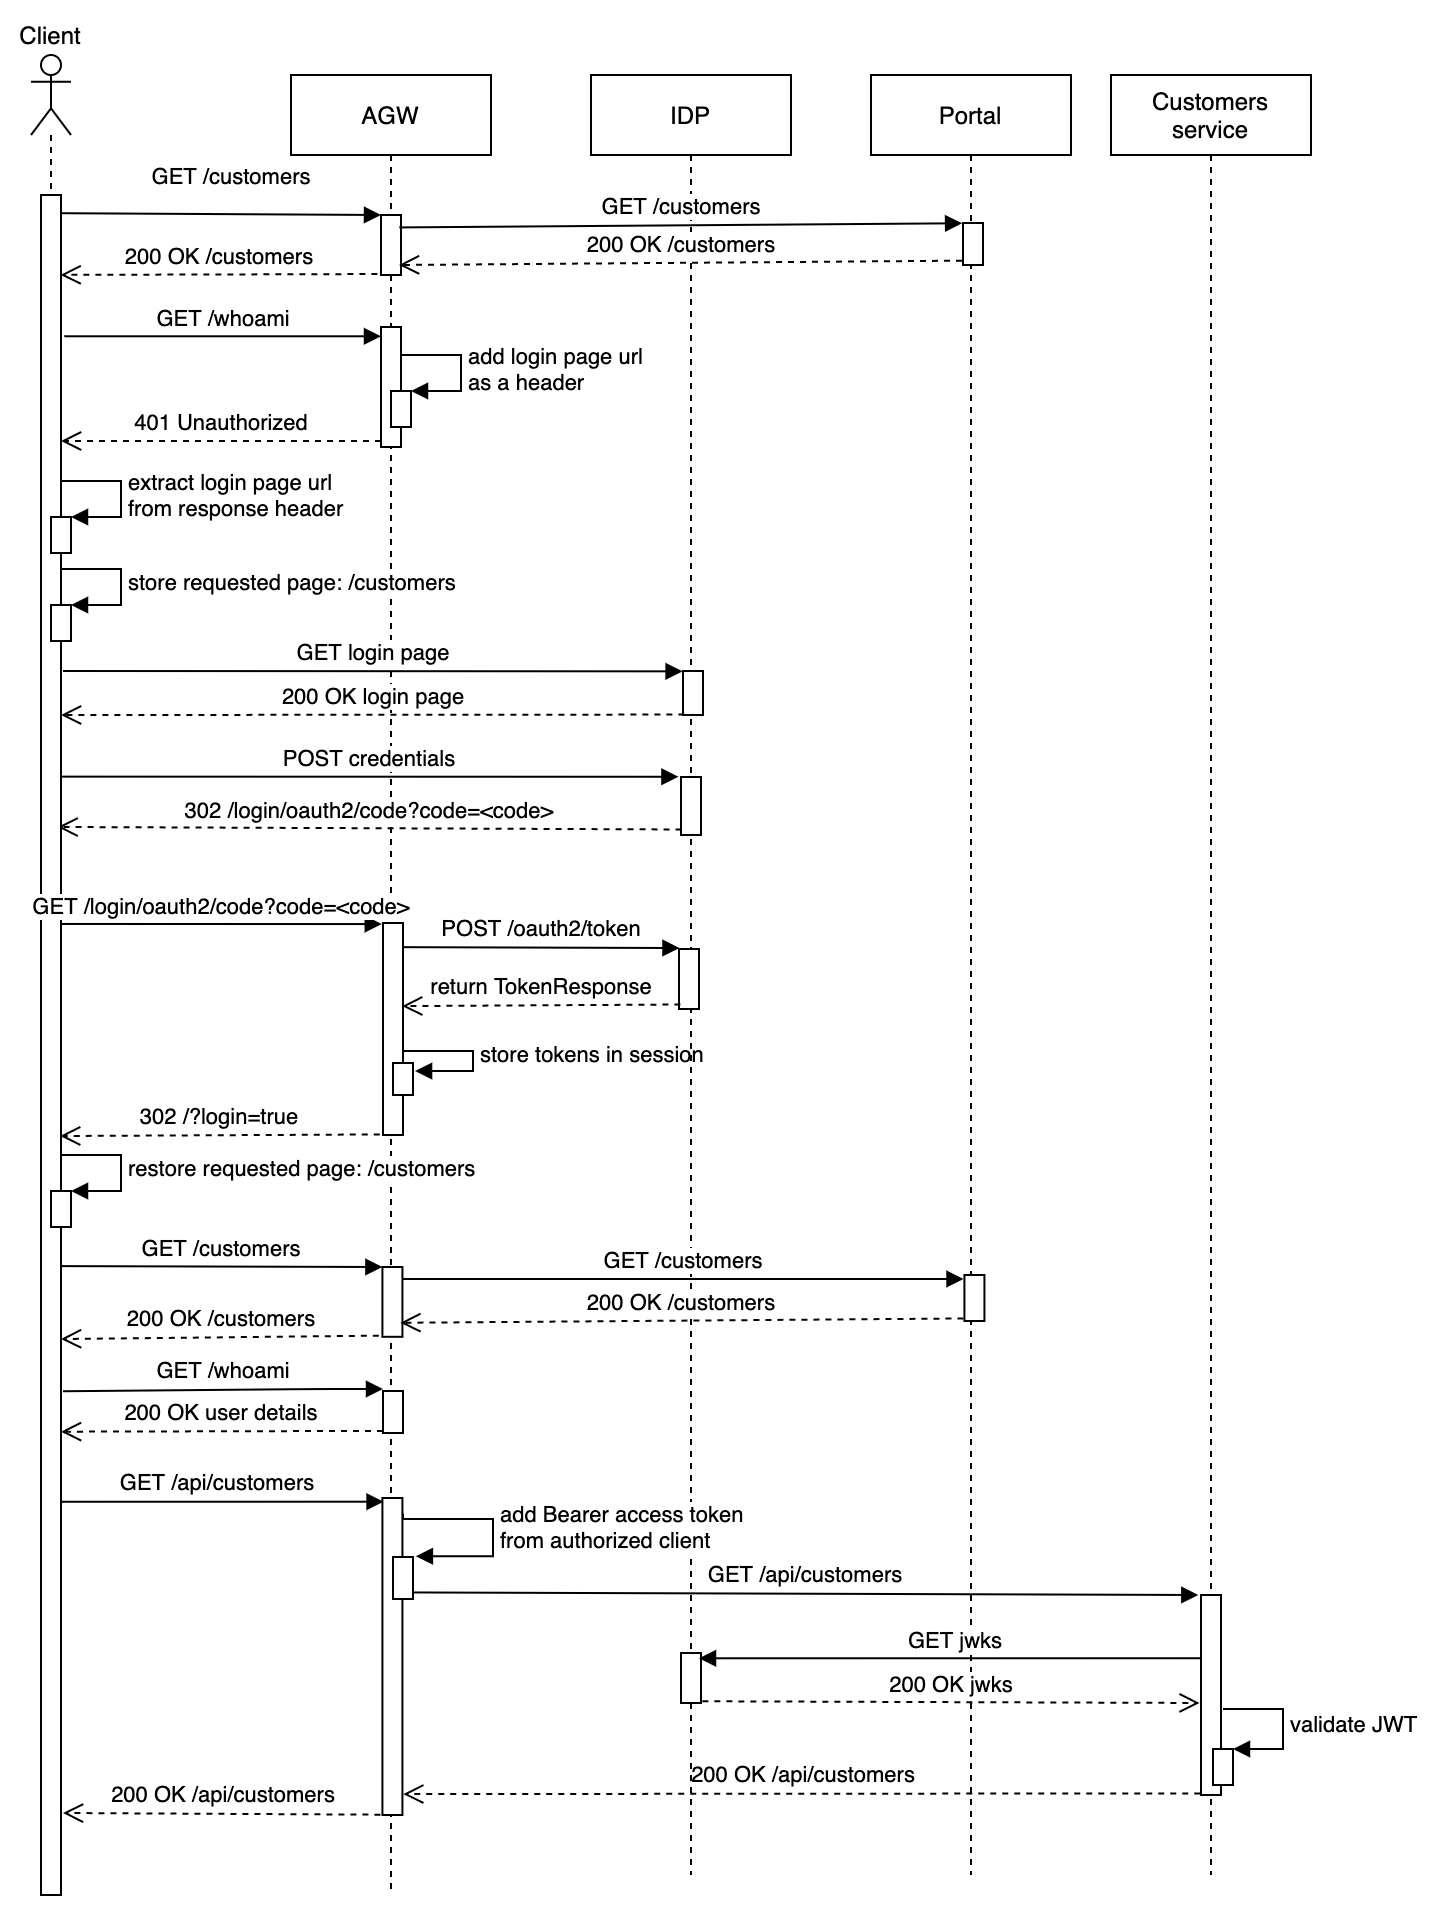
OAuth2 Authentication With API Gateway In A Distributed Environment Blog

This is the standard three step OAuth 2 authentication scheme As the user you are the resource owner the client application is the web portal the authorization service is Keycloak and the resource server is a set of microservices Here is an example of a standard Keycloak login URL you can see the realm and the client

1 Planning for securing applications and services Edit this section Report an issue As an OAuth2 OpenID Connect and SAML compliant server Keycloak can secure any application and service as long as the technology stack they are using supports any of these protocols

Keycloak is based on a set of administrative UIs and a RESTful API and provides the necessary means to create permissions for your protected resources and scopes associate those permissions with authorization policies and enforce authorization decisions in your applications and services

Overview In this tutorial we ll discuss the basics of setting up a Keycloak server and connecting a Spring Boot application to it using Spring Security OAuth2 0 Further reading Spring Security and OpenID Connect Learn how to set up OpenID Connect from Google with a simple Spring Security application Read more

Authentication Flows The starting point in our process to secure an application or a web service with Keycloak is to identify and authenticate the user The sequence of actions a user or a service needs to perform to be authenticated in Keycloak is called authentication flow
Features Single Sign On Identity Brokering and Social Login User Federation Admin Console Account Management Console Authorization Services See https www keycloak Ideas behind Keycloak AuthServices Authentication Keycloak is OAuth2 OpenID Connect compliant provider so it should be easy to use it 5 Keycloak Endpoints Keycloak exposes a variety of REST endpoints for OAuth 2 0 flows To use these endpoints with Postman we ll start by creating an Environment called Keycloak Then we ll add some key value entries for the Keycloak authorization server URL the realm OAuth 2 0 client id and client password
REST API authentication using Keycloak This section describes the way Keycloak acts as an authentication module that gives a temporary token to the consumer This temporary token can then be used by a resource to verify if the request is from an authenticated source It is assumed that you have set up Keycloak on a system and have admin access