Interactive Application Security Testing Interactive Application Security Testing Checkmarx IAST Checkmarx Redefining interactive Application Security Testing Interactive Application Security Testing Is The Next Big Thing In IAST Interactive Application Security Testing Mend What Is IAST Interactive Application Security Testing Acunetix Web Interactive application security testing IAST combines static application security testing SAST with dynamic application security testing DAST to create a synergistic and self learning interactive application security testing approach
Web Oct 4 2018 nbsp 0183 32 Interactive Application Security Testing IAST Tools Primarily for web apps and web APIs Keeping Open Source libraries up to date to avoid Using Components with Known Vulnerabilities OWASP Top 10 2017 A9 Static Code Quality Tools Disclaimer OWASP does not endorse any of the Vendors or Scanning Tools by listing them below Web Jun 21 2023 nbsp 0183 32 Many organizations use interactive application security testing IAST tools to get rid of security vulnerabilities SAST DAST and IAST are the testing methods that organizations use to carry out effective security testing on their applications There are tools available in the market for each type of testing process
What Is IAST Interactive Application Security Testing Acunetix Interactive Application Security Testing IAST Seeker Interactive Application Security Testing IAST Synopsys Interactive Application Security Testing IAST Over Static SAST And Seeker Interactive Application Security Testing IAST Synopsys What Is IAST Interactive Application Security Testing Essential Aspects To Know About Interactive Application Security Testing Interactive Application Security Testing IAST YouTube What Is Interactive Application Security Testing IAST SNS Blog
Interactive Application Security Testing
 Interactive Application Security Testing
https://checkmarx.com/wp-content/uploads/2021/04/Screen-Shot-2021-06-28-at-12.46.34-PM-915x572.png
Web This is where interactive security application testing comes in IAST works through software instrumentation or the use of instruments to monitor an application as it runs and gather information about what it does and how it performs
Templates are pre-designed documents or files that can be used for numerous purposes. They can conserve time and effort by offering a ready-made format and design for producing different sort of content. Templates can be used for individual or expert tasks, such as resumes, invites, flyers, newsletters, reports, discussions, and more.
Interactive Application Security Testing

Interactive Application Security Testing Synopsys

Interactive Application Security Testing IAST

Seeker Interactive Application Security Testing IAST Synopsys

Interactive Application Security Testing IAST Over Static SAST And
What Is IAST Interactive Application Security Testing

Essential Aspects To Know About Interactive Application Security Testing

Web Interactive Application Security Testing IAST interactive application security testing analyzes code for security vulnerabilities while the app is run by an automated test human tester or any activity interacting with the application functionality

Web What Is Interactive Application Security Testing Interactive application security testing IAST is an application security testing method that tests your application for vulnerabilities in execution while the app is actually being used either by a real user or an automated test runner

Web Interactive application security testing abbreviated as IAST is a security testing method that detects software vulnerabilities by interaction with the program coupled with observation and sensors The tool was launched by
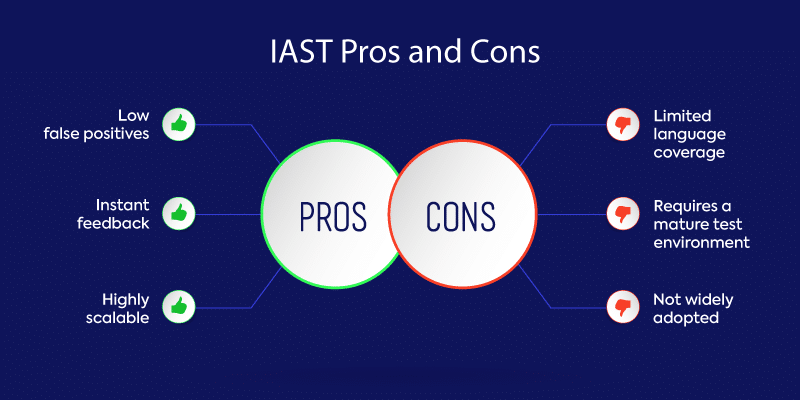
Web Types of interactive application security testing tools Passive IAST Most tools provide only a sensor that attaches to the running application If this sensor notices Active IAST A large selection of IAST tools on the market are delivered by DAST makers but as separate non integrated True

Web Easily identify vulnerabilities in real time across all layers of the application stack Eliminate false positives with fast accurate detection of real security risks with automated validation Give developers vulnerability lists prioritized by risk to easily focus on what matters most
[desc-11] [desc-12]
[desc-13]